A kit built on your name

The actor behind a phishing kit, the thread that sells it and the lookalike domain, defanged so nothing opens by accident.
Watch terms
- Rheinmark
- Nordhafen Bank
CTI, SOC, fraud, incident response and third-party risk teams work from the same captured evidence, each with the view it needs.
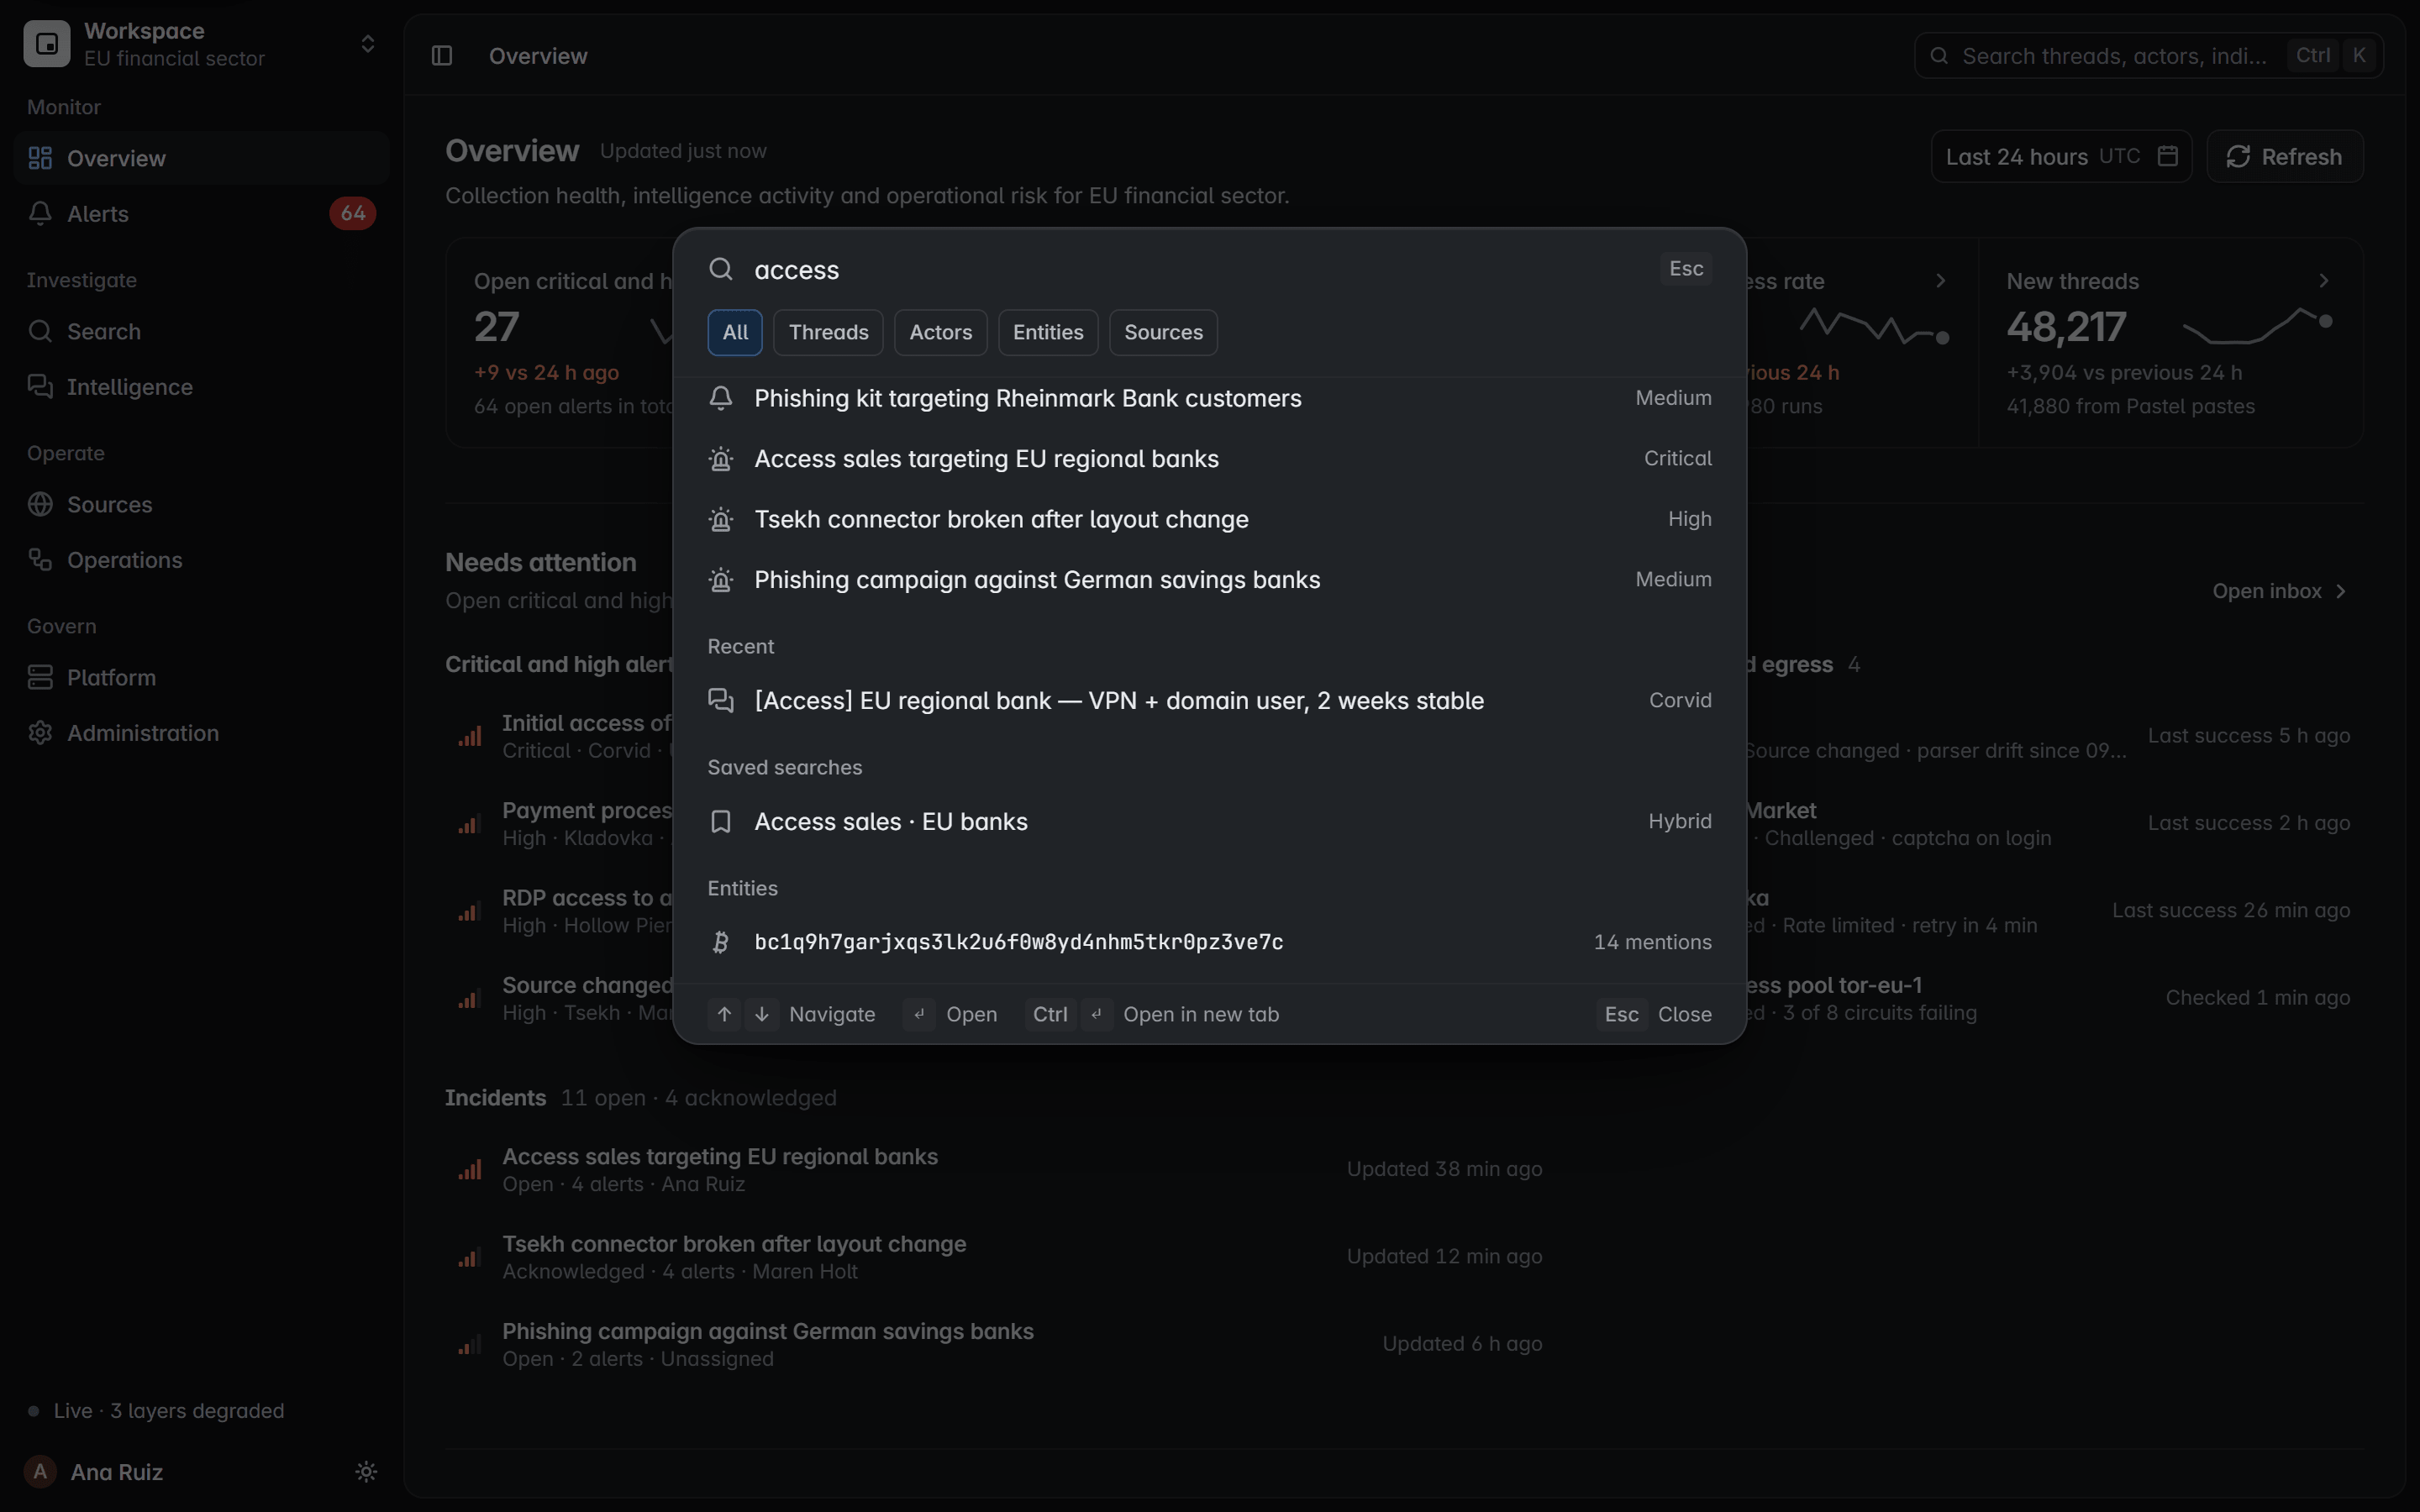
One console and the same sealed evidence, read five ways. Pick a team to see the screen its day starts from.
Follow actors, leaks and access sales across sources, with evidence attached to every report.

Get early warning when your domains, infrastructure, credentials or brand appear in underground conversations.
Catch data sales, impersonation and offers that target your customers.
Reconstruct what was said, when and by whom, from sealed captures.
Know when suppliers or partners appear on ransomware leak sites.
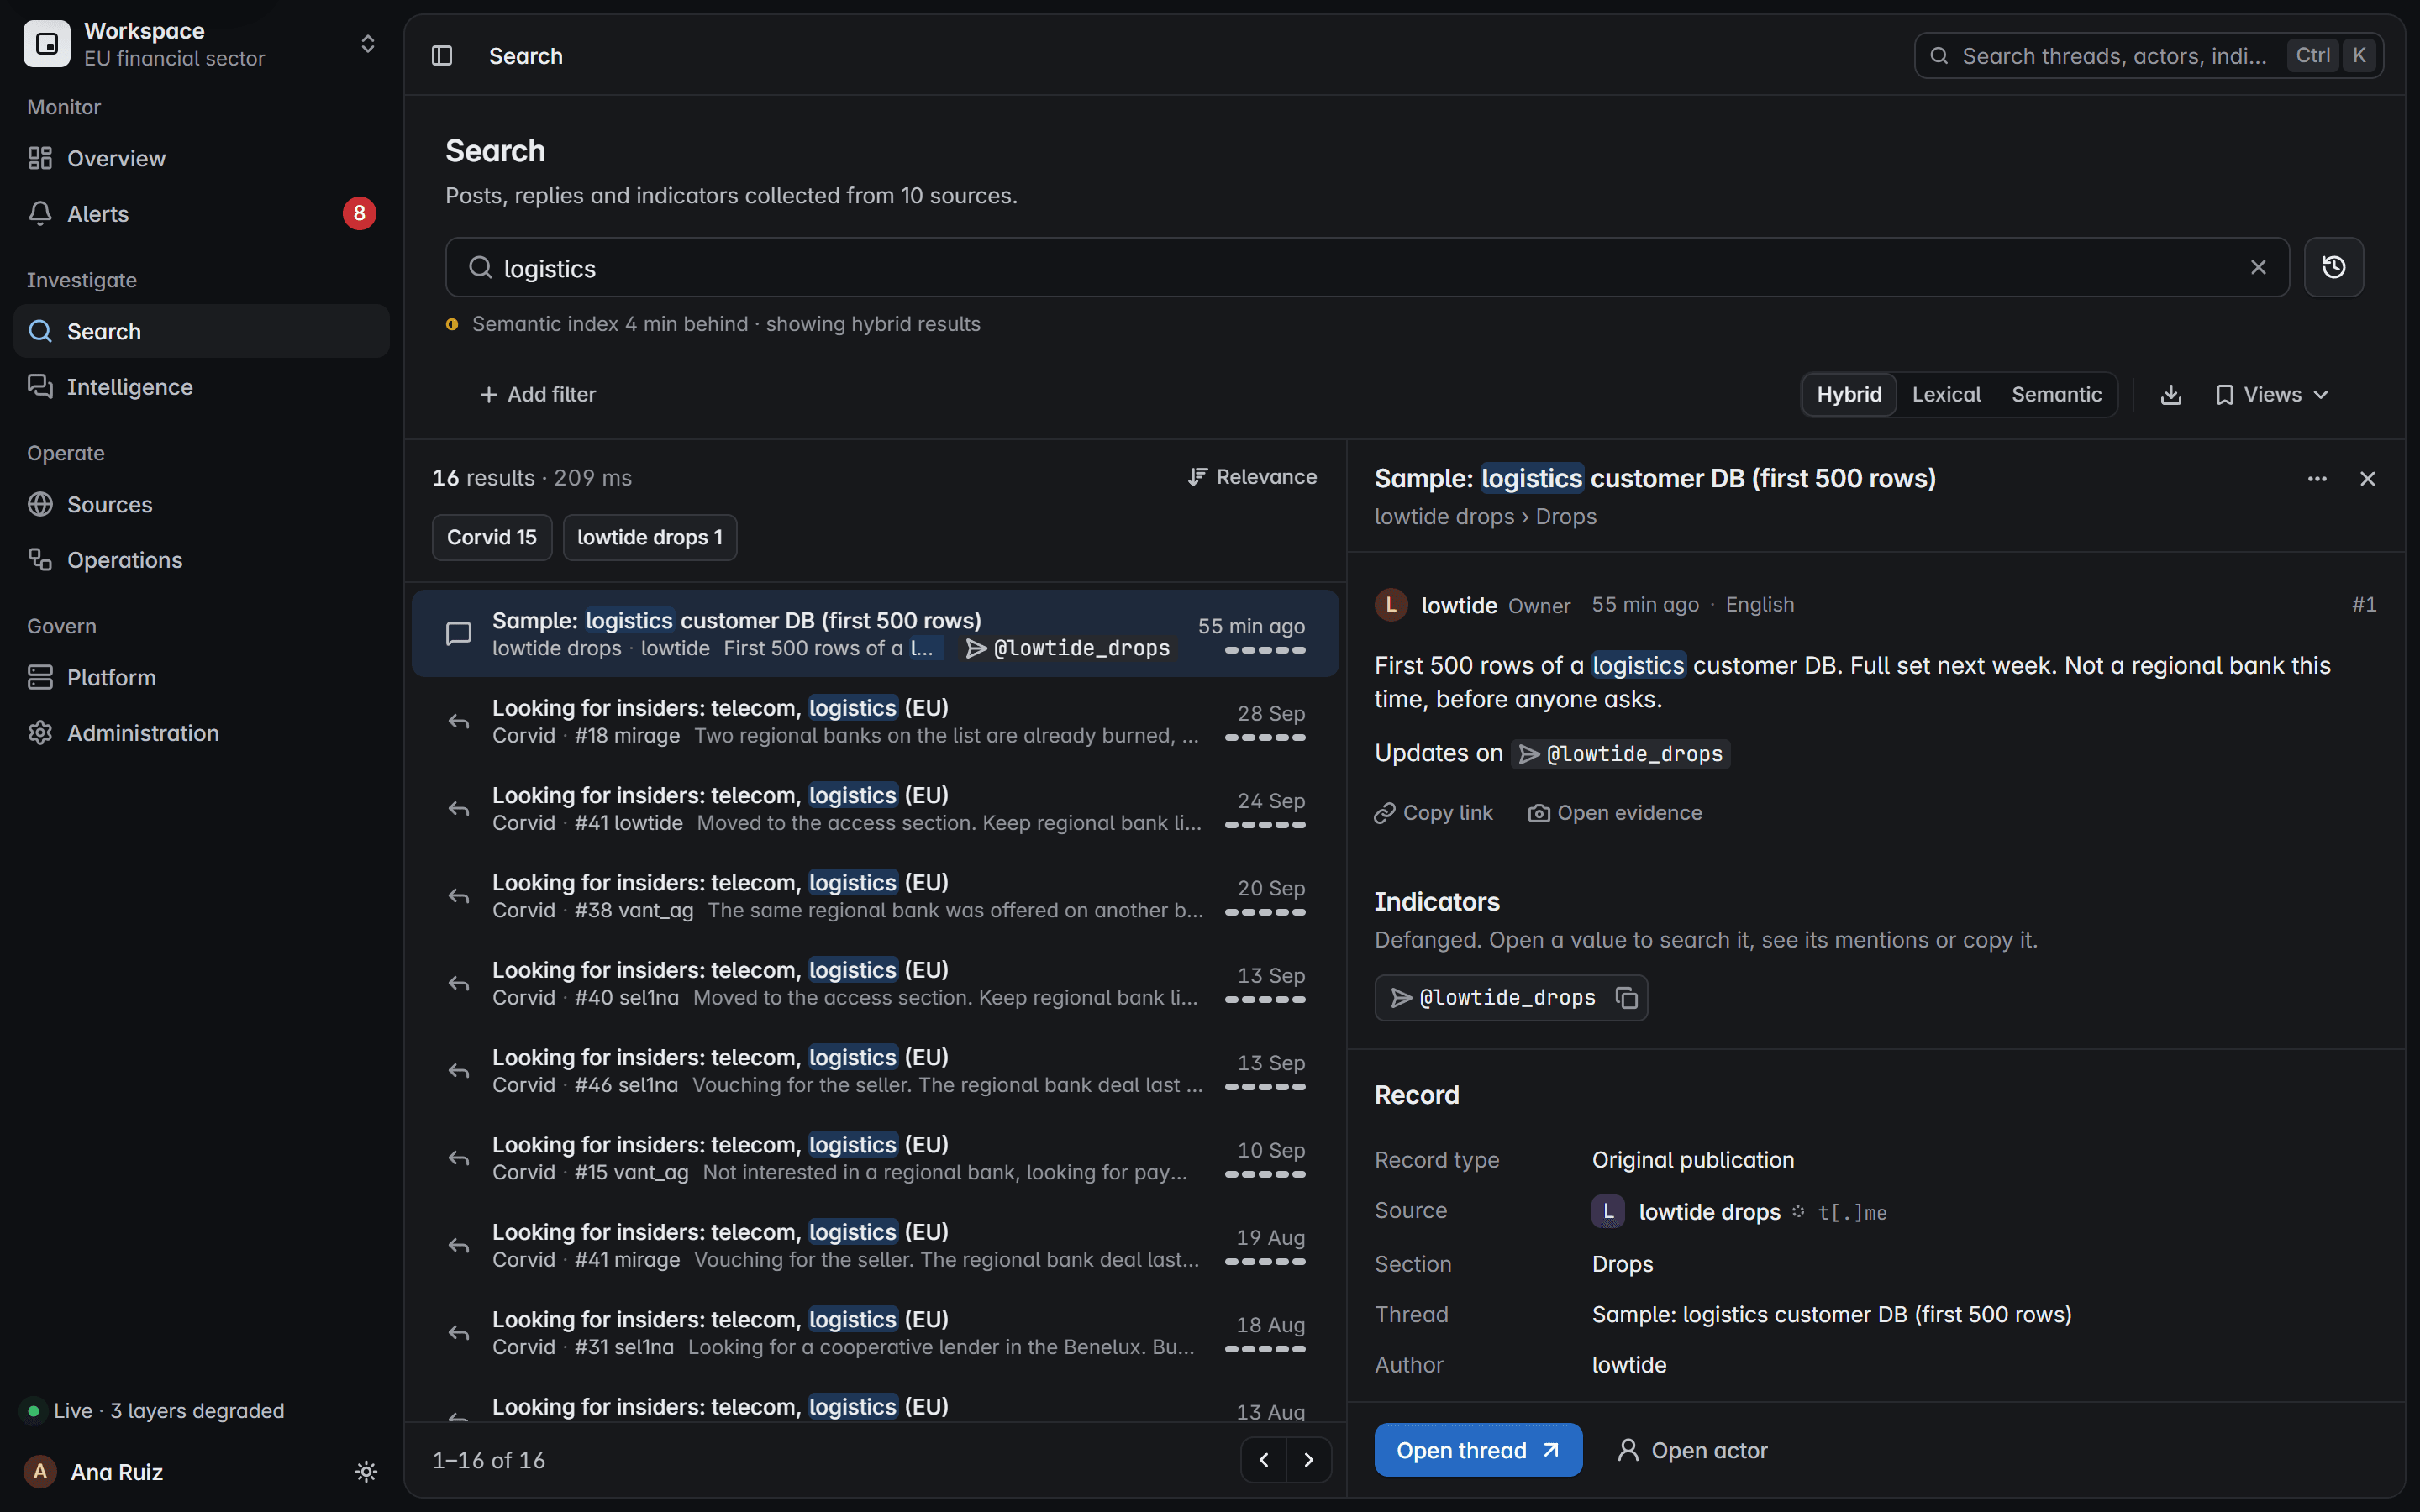
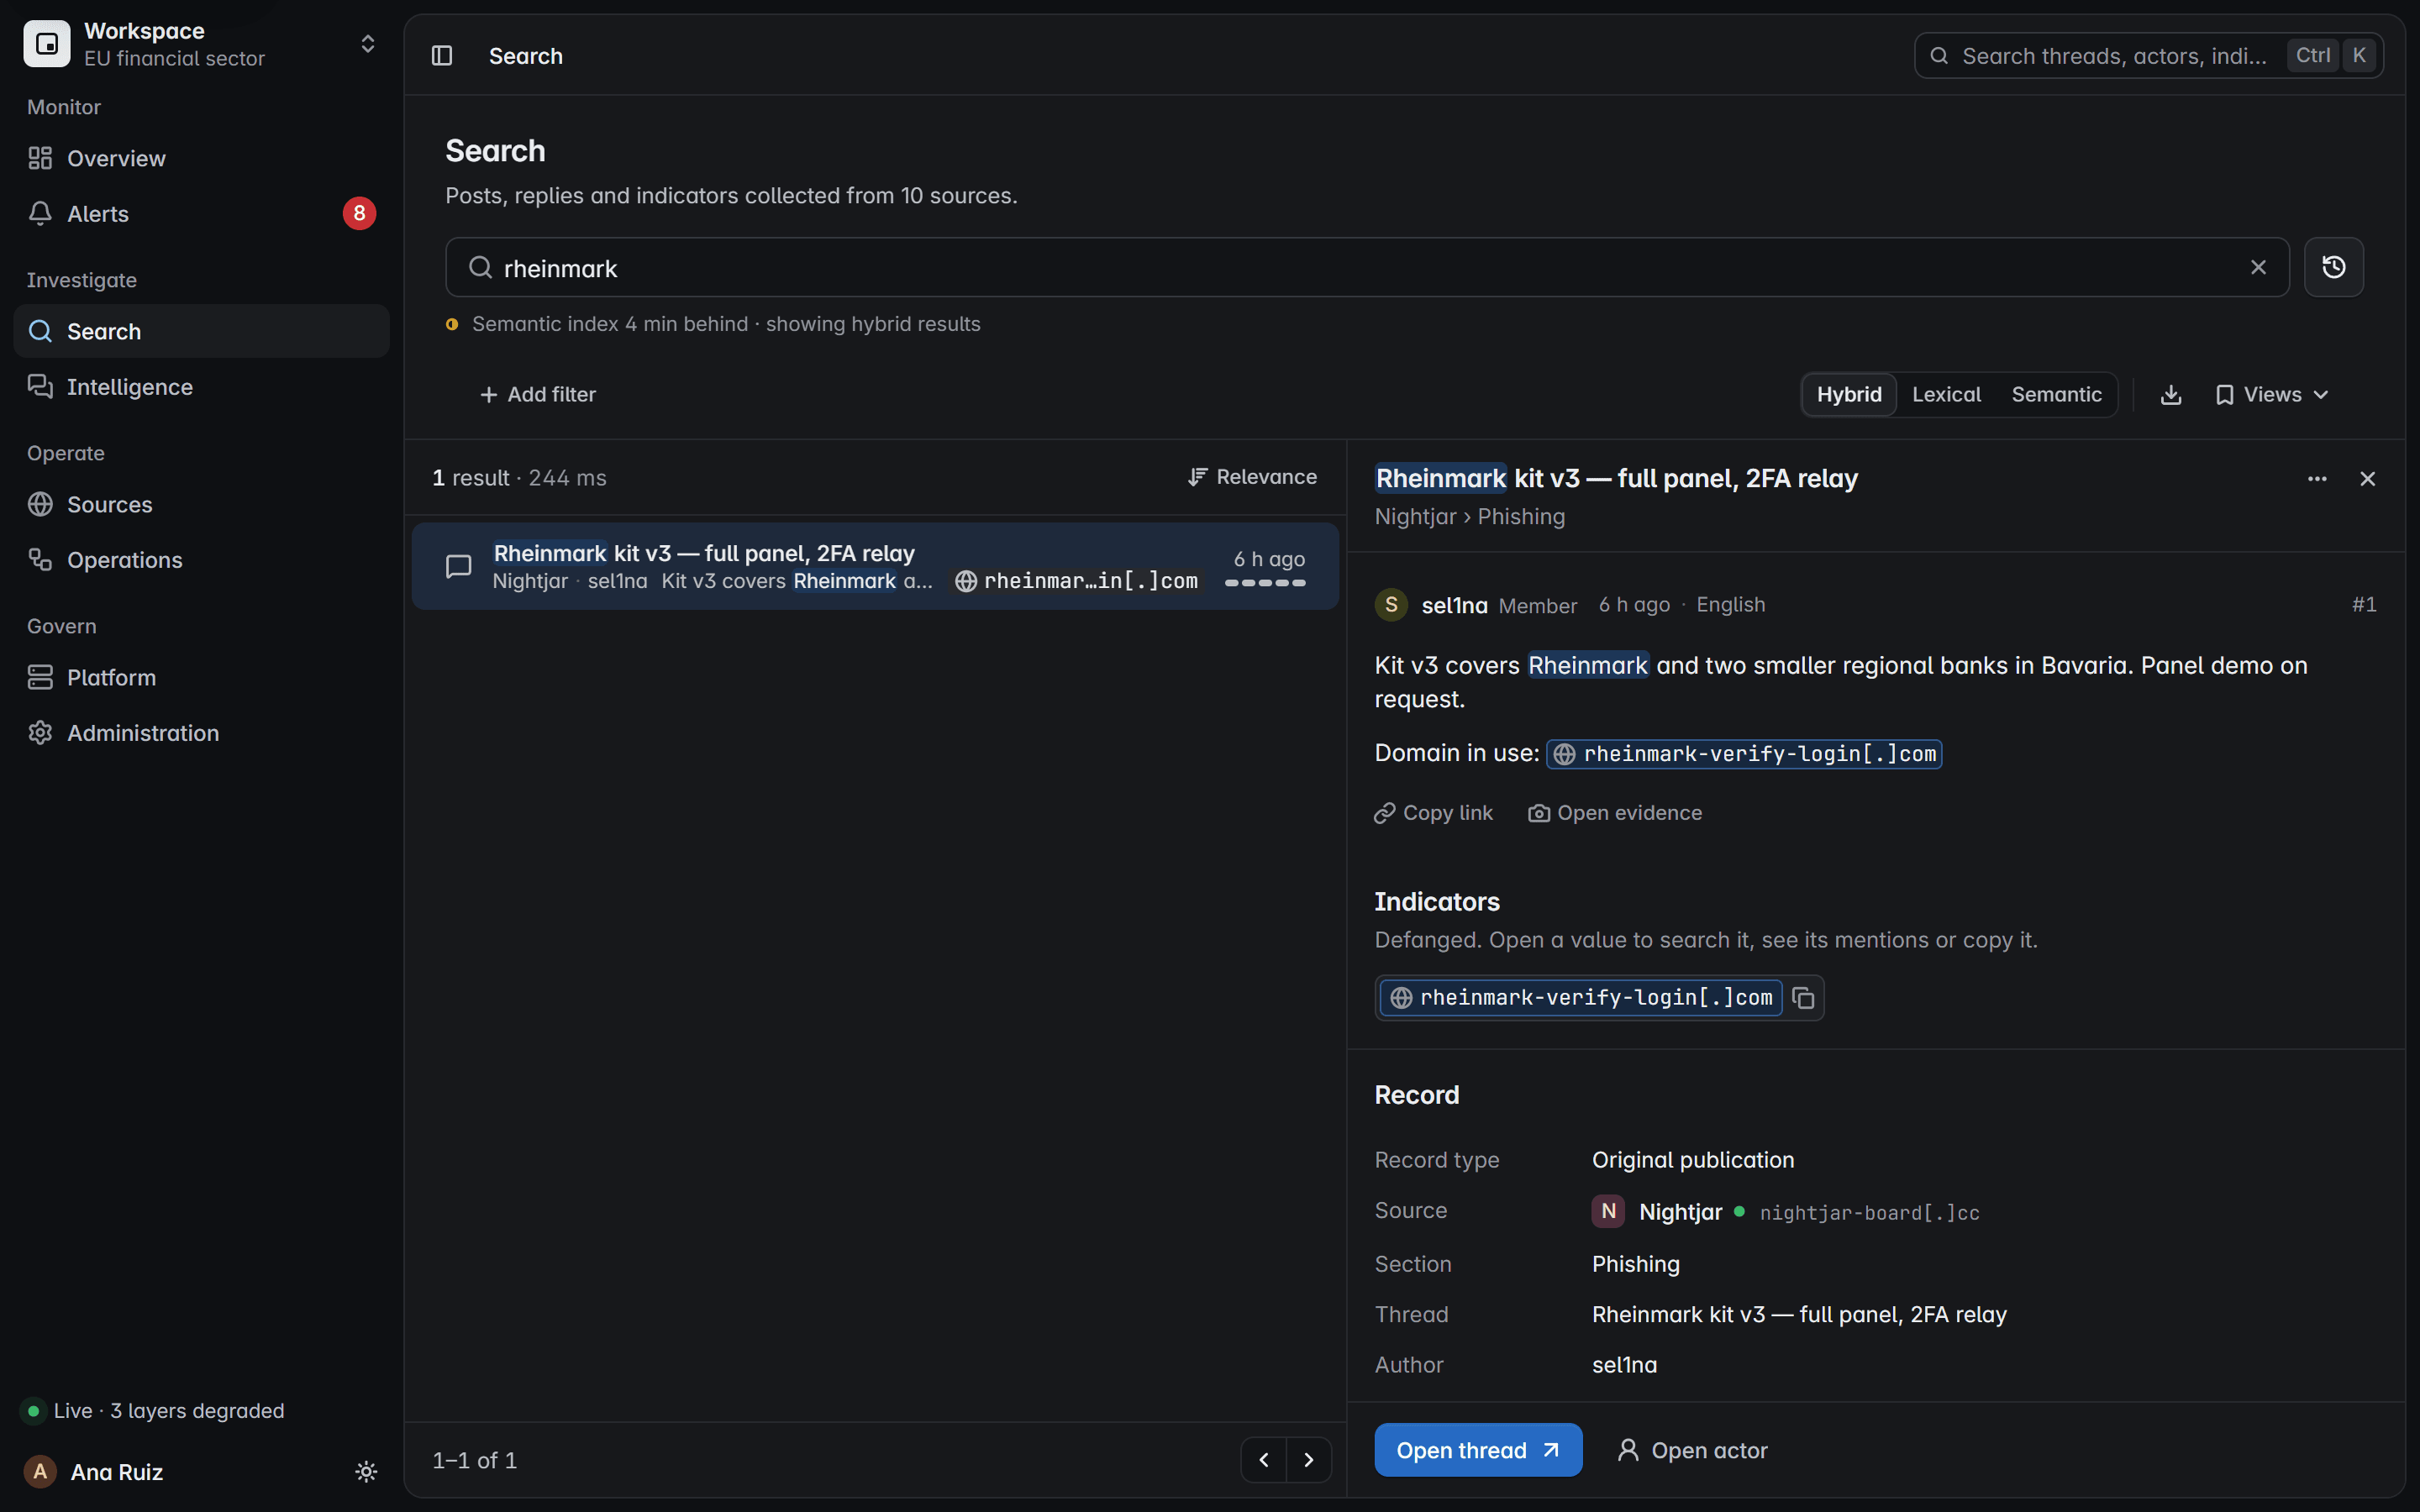
A saved search surfaces the post. The profile joins the author’s other names, forums and contacts, and the report leaves with its evidence.

Saved search
Saved searches keep the query, the mode and the filters, and everyone in the workspace can open them.
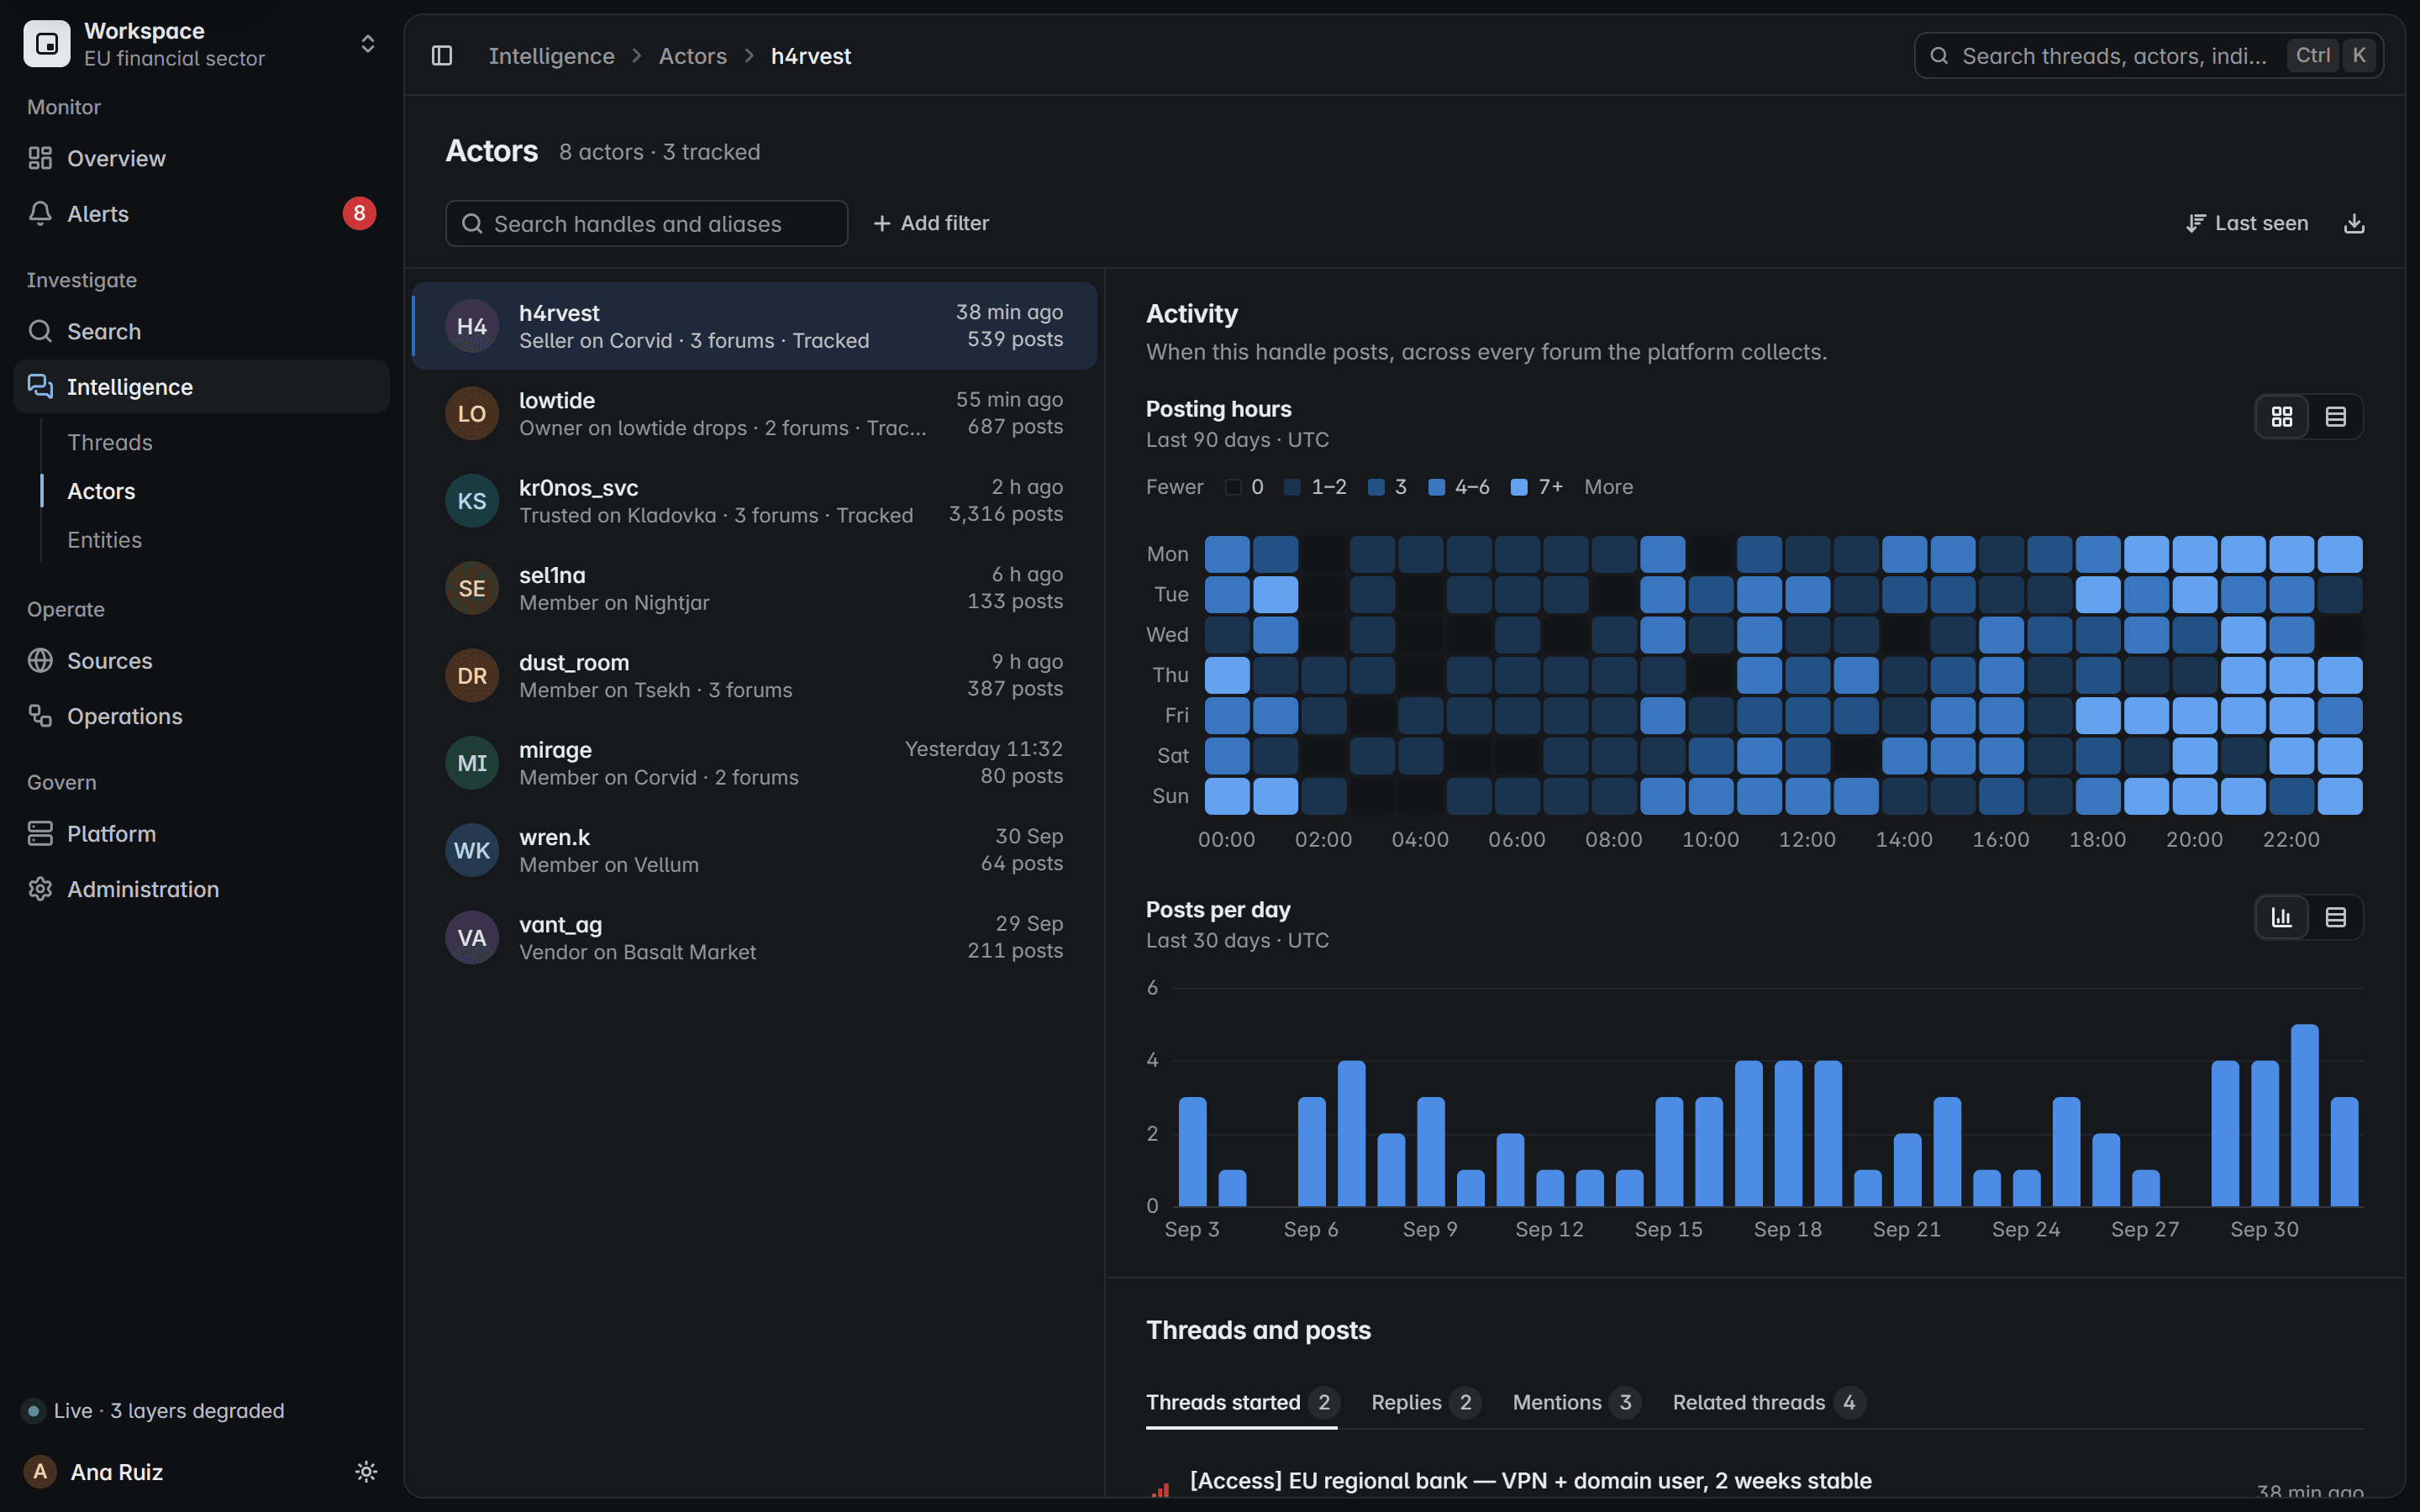
Activity
Posting hours and posts per day, across every forum the platform collects, always in UTC.
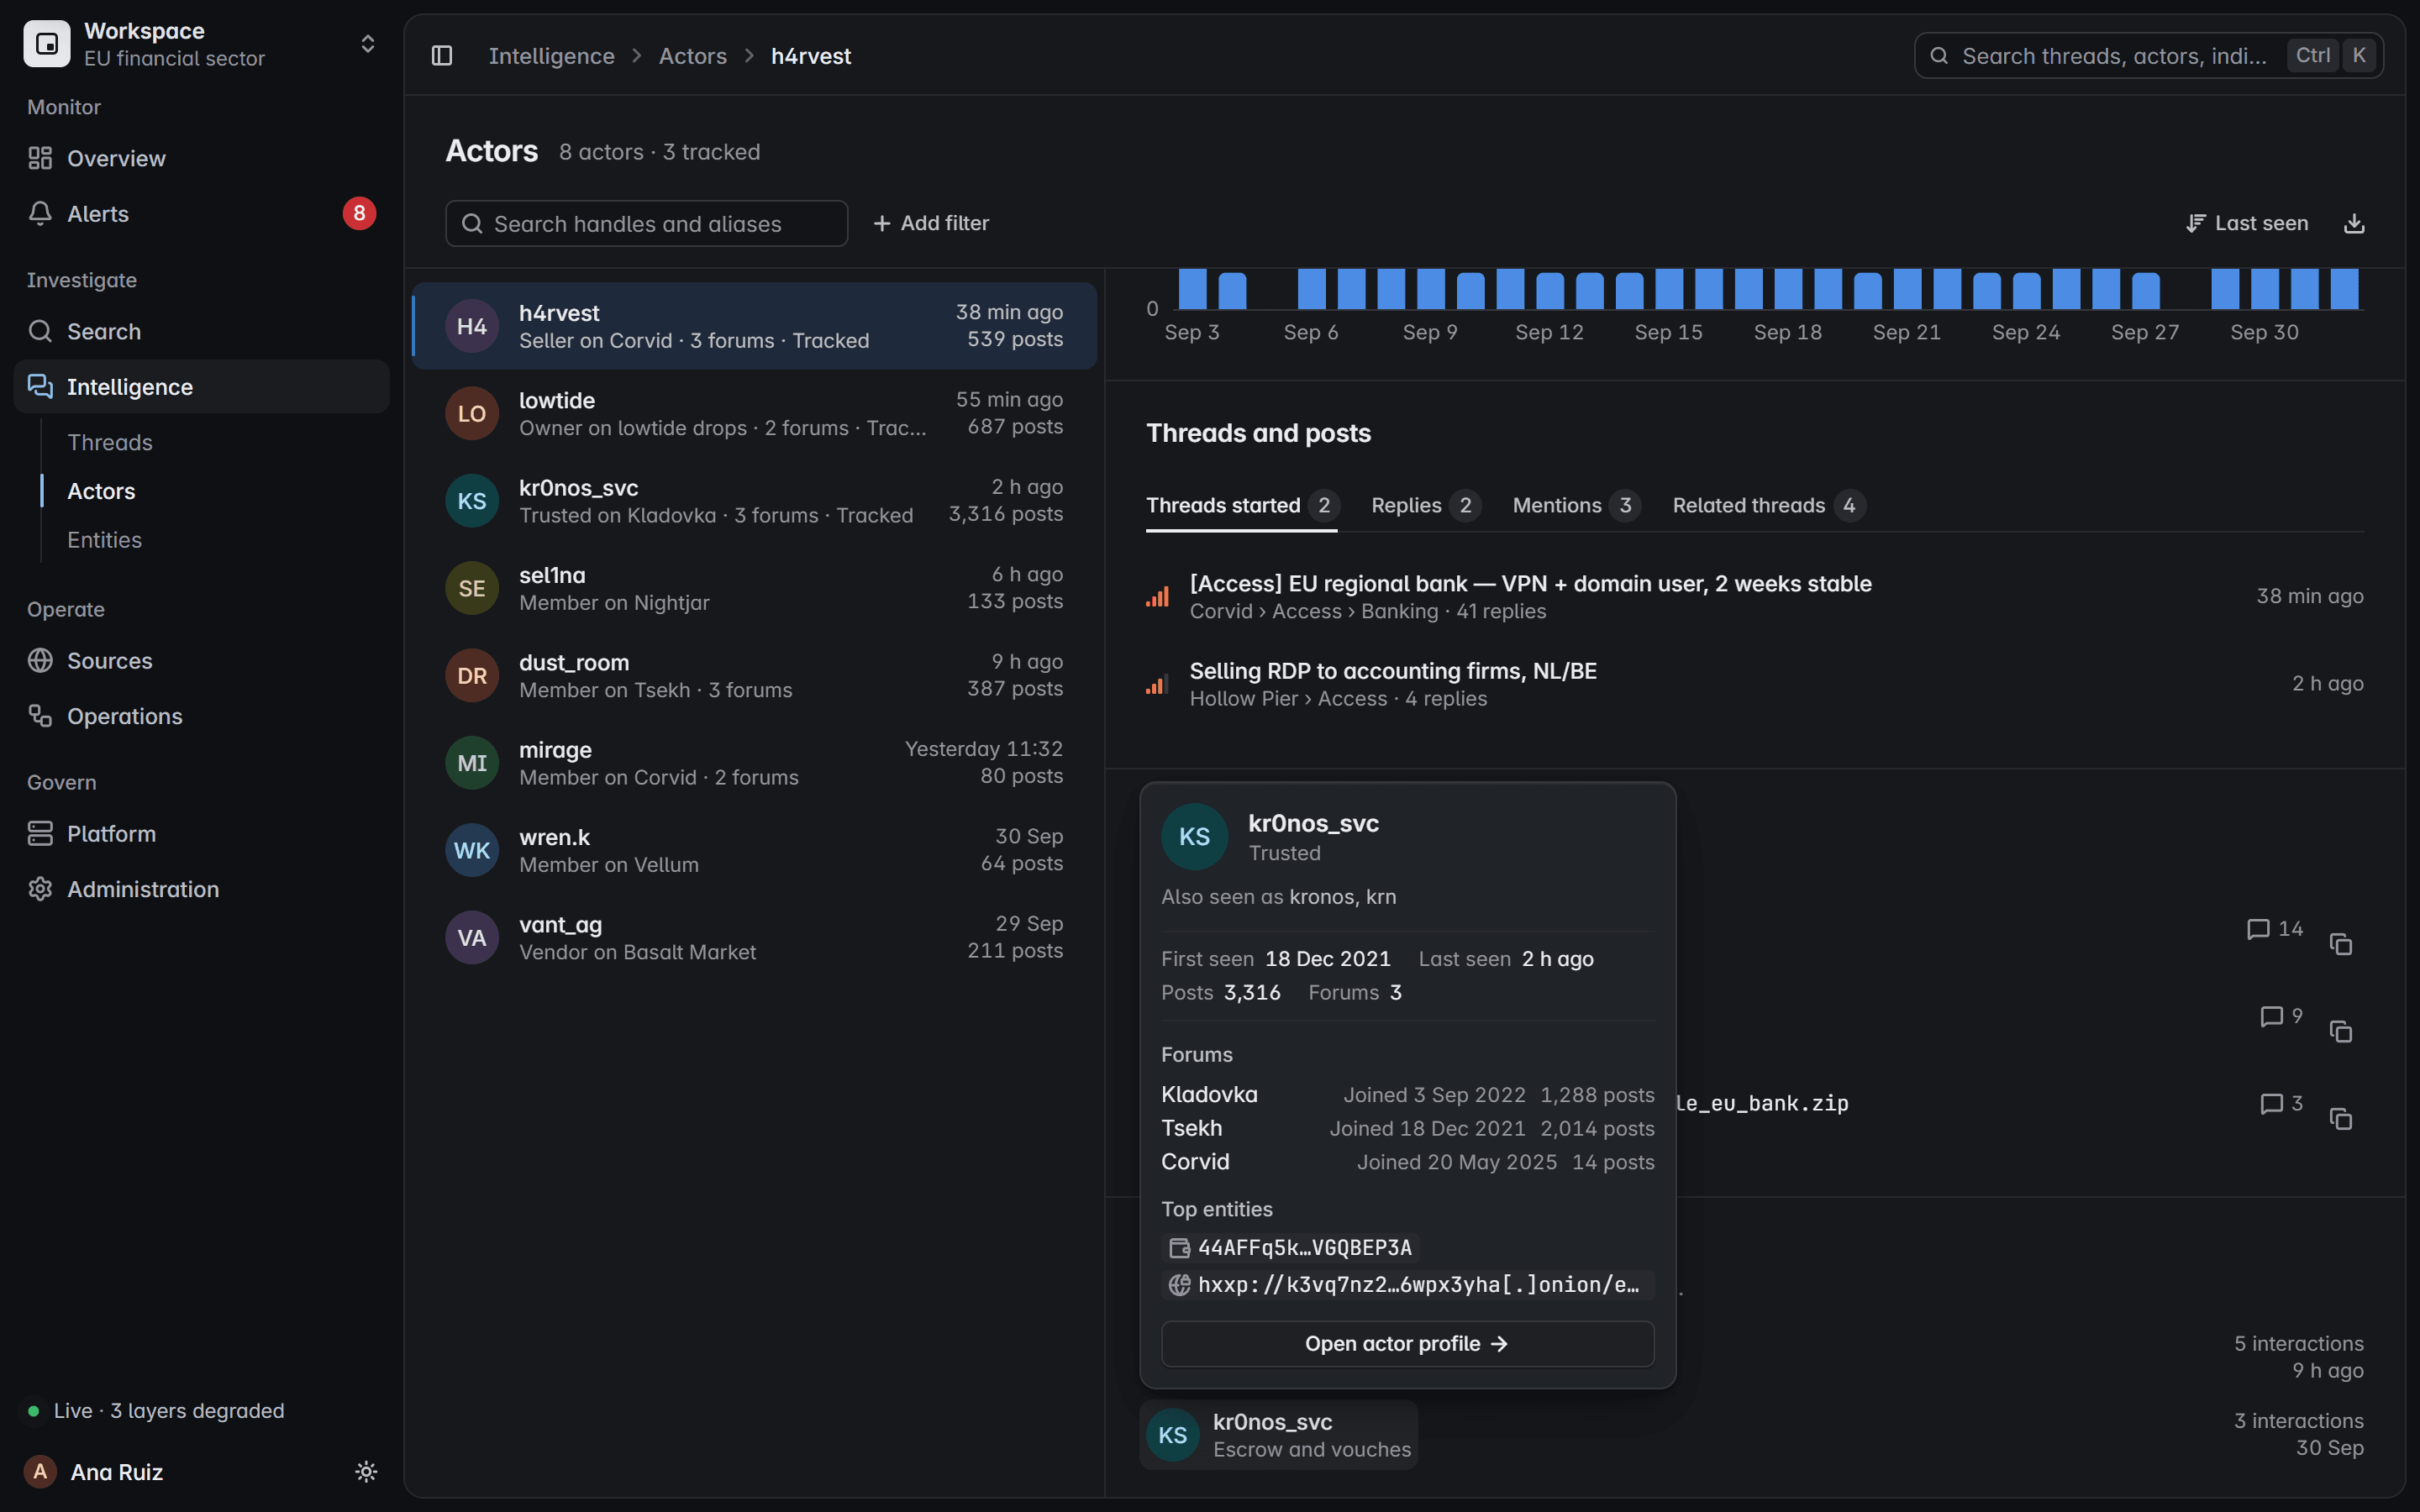
Counterparties
Counterparties come from replies, quotes and vouches in stored threads, each with its own aliases, forums and indicators.
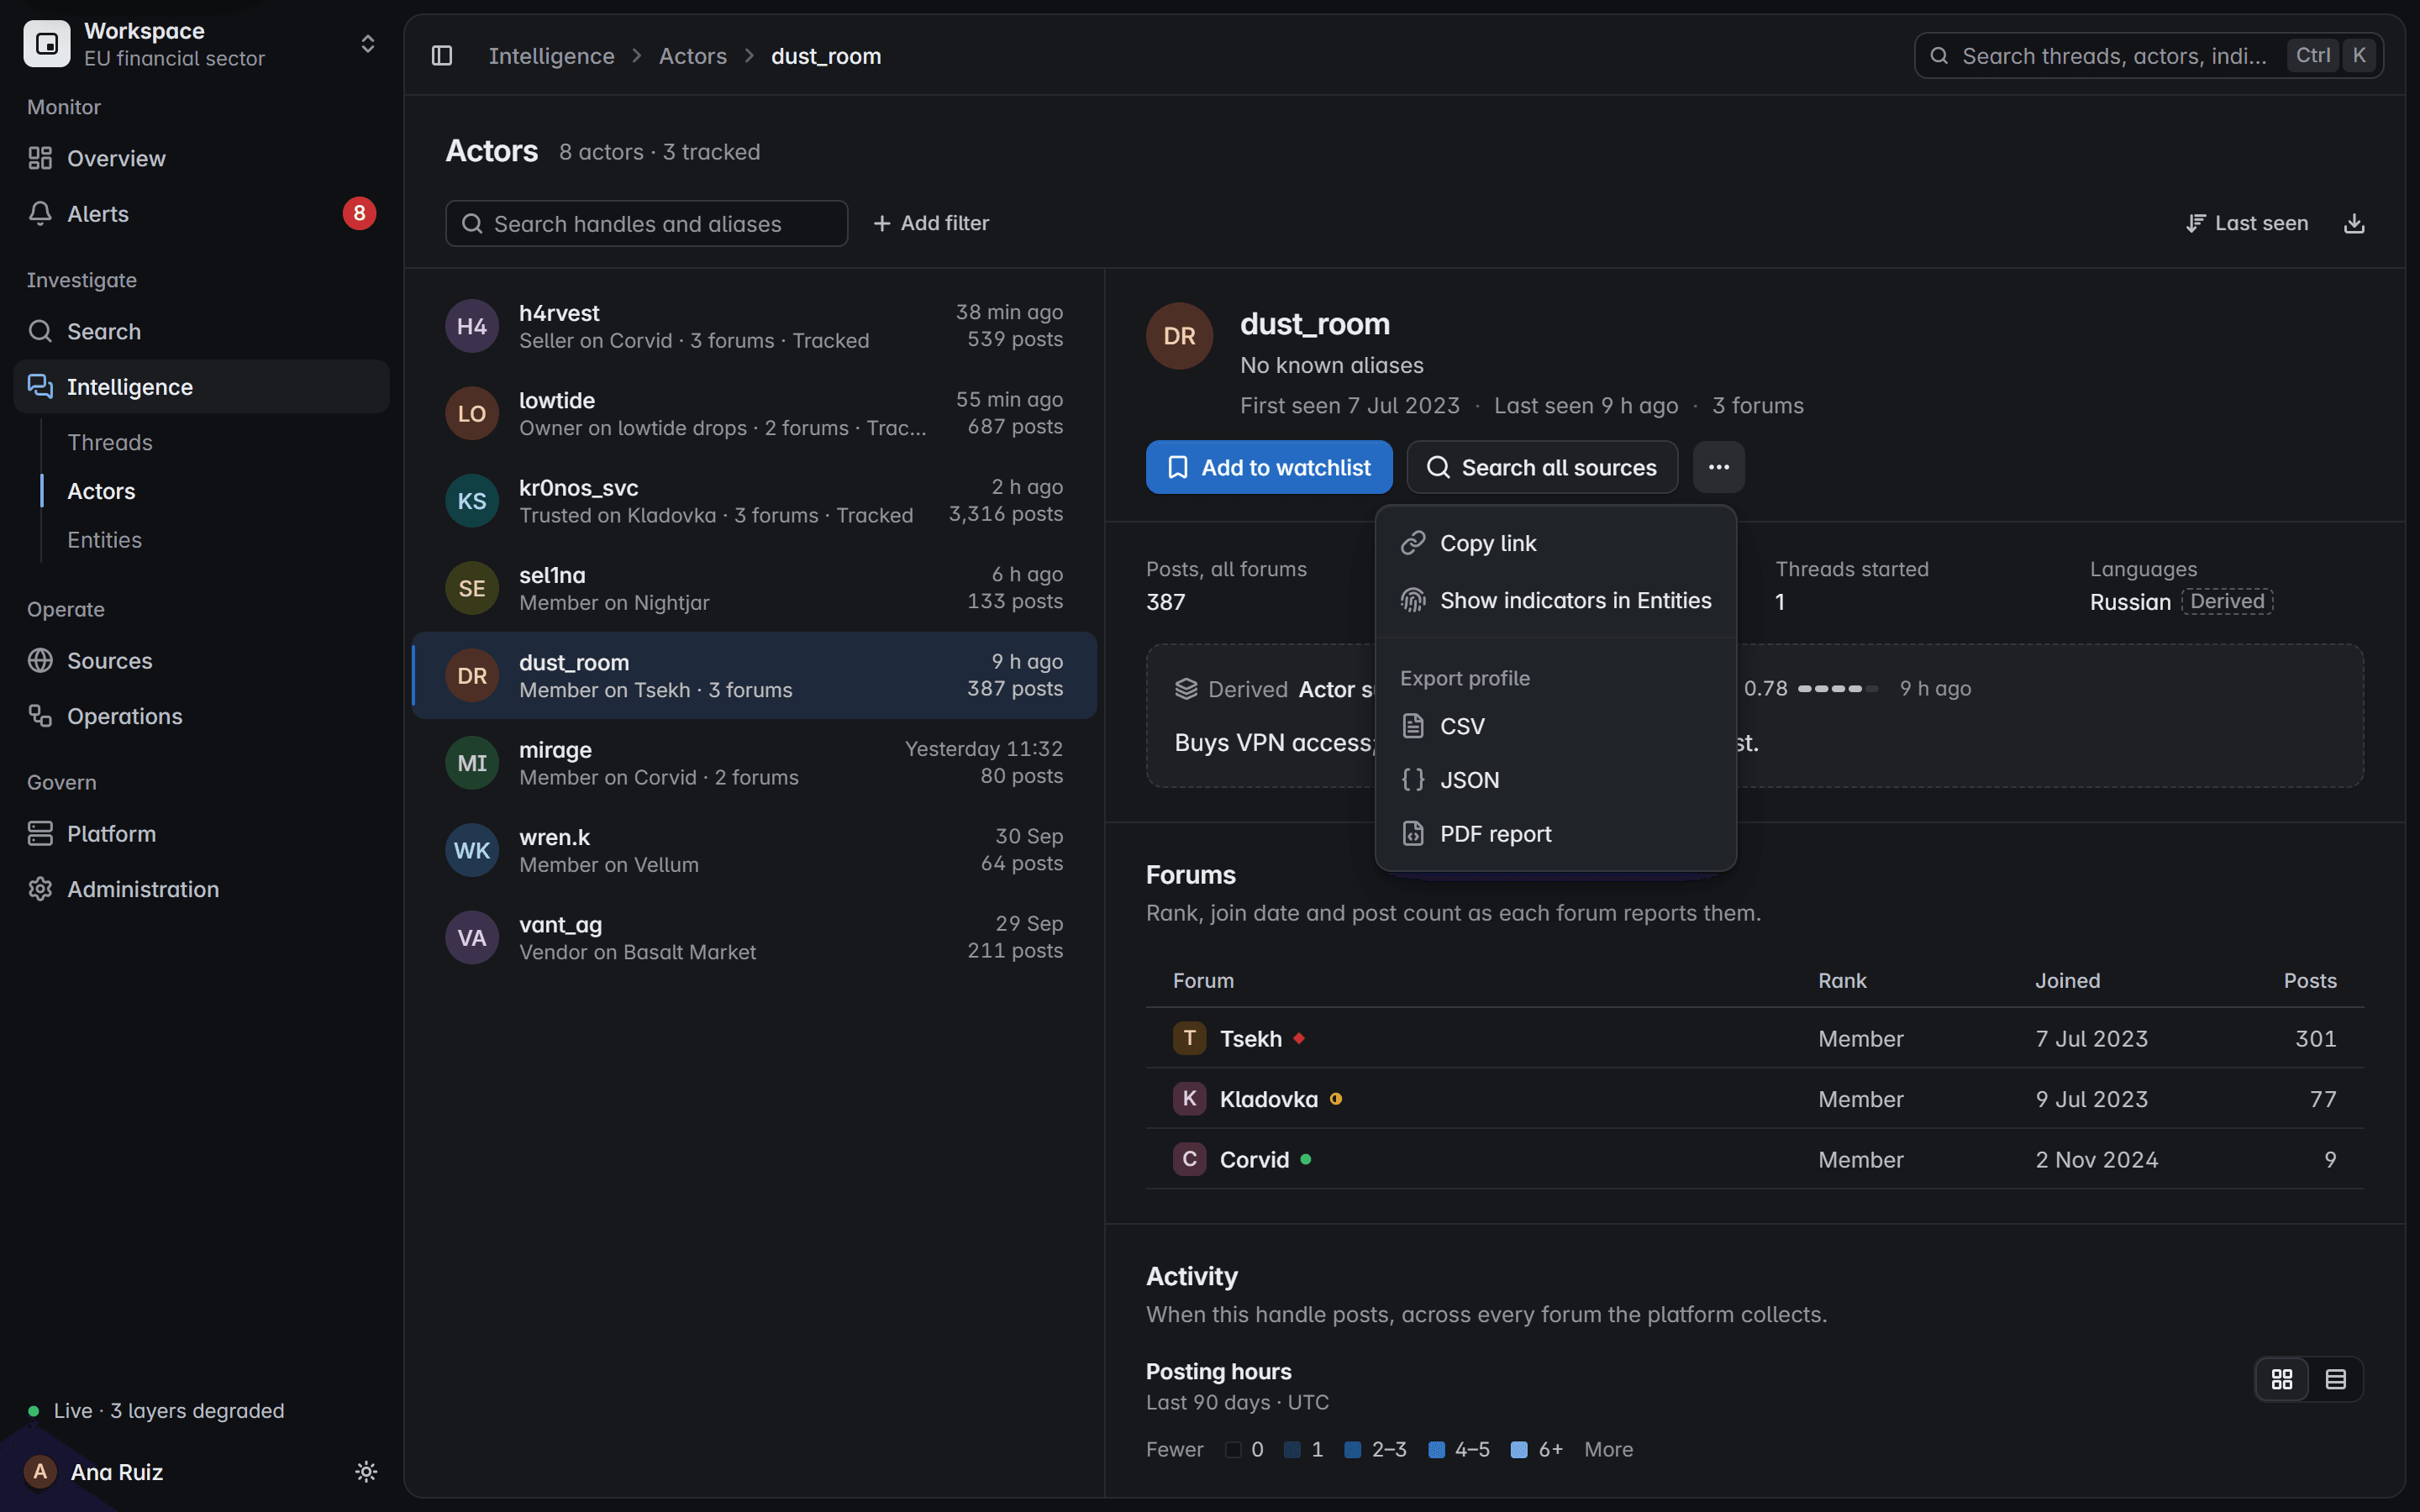
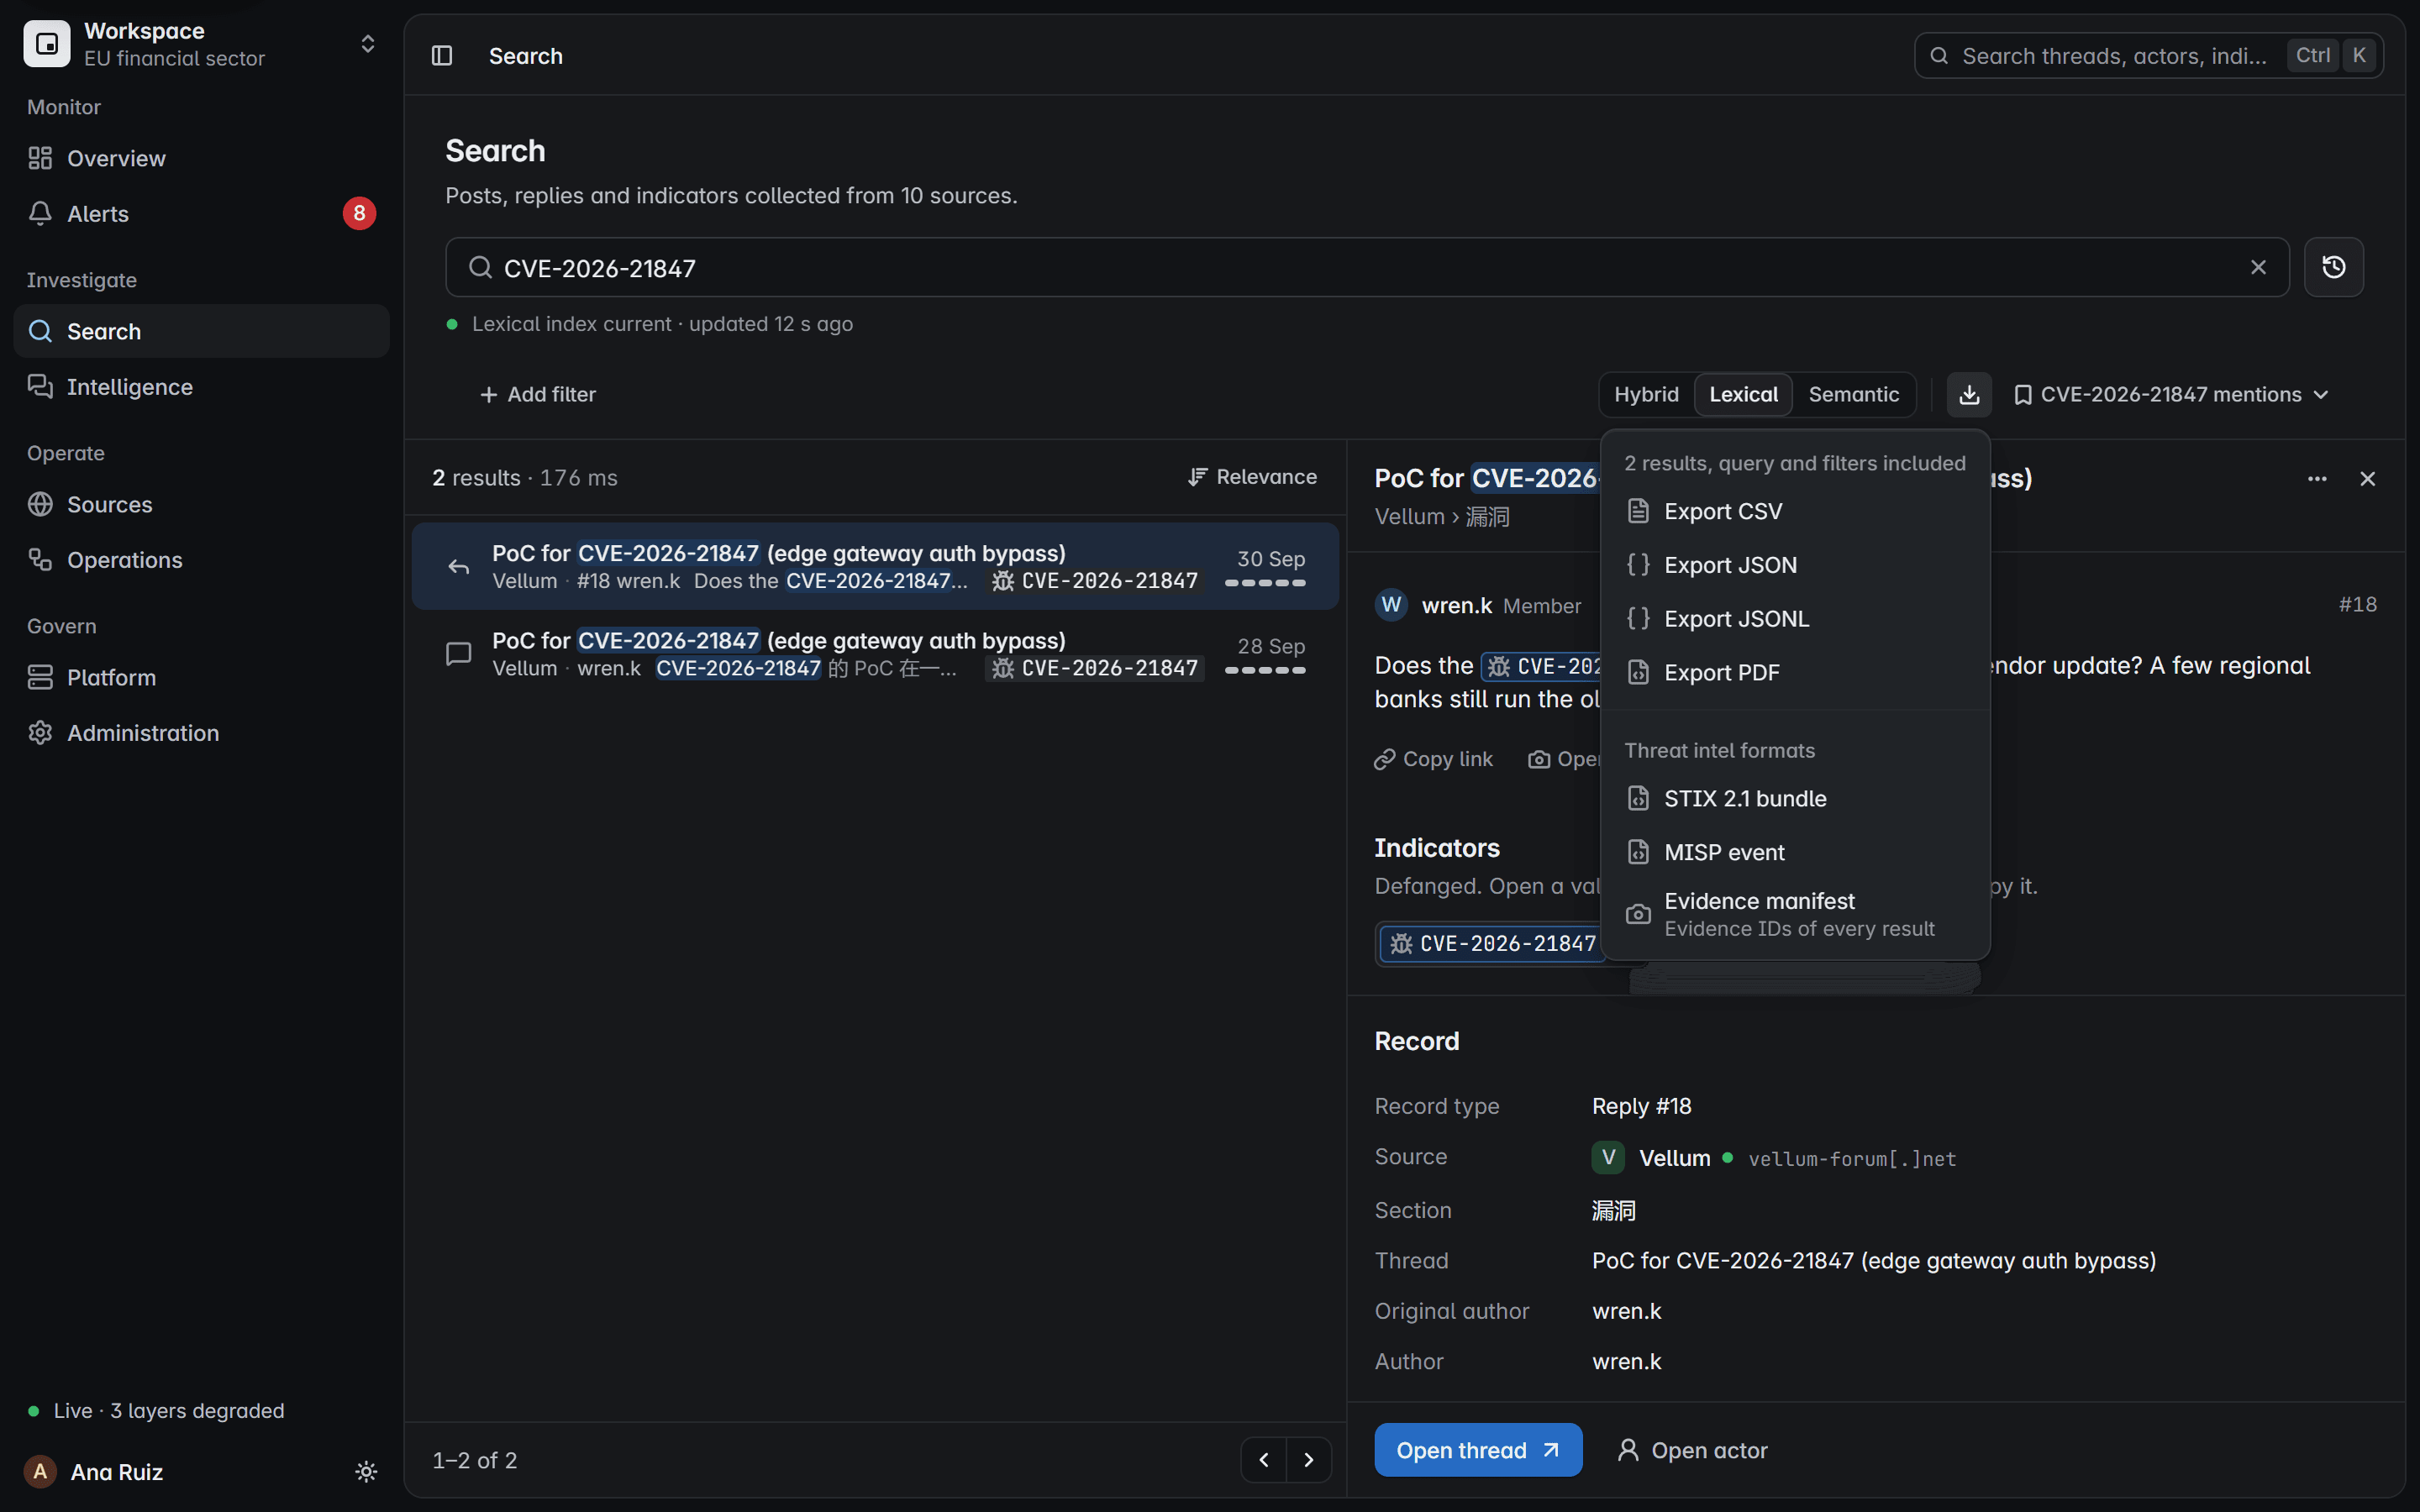
Export
Export identity, forums, activity, posts and indicators as CSV, JSON or a PDF report, with timestamps in UTC.
Product screen with fictional data
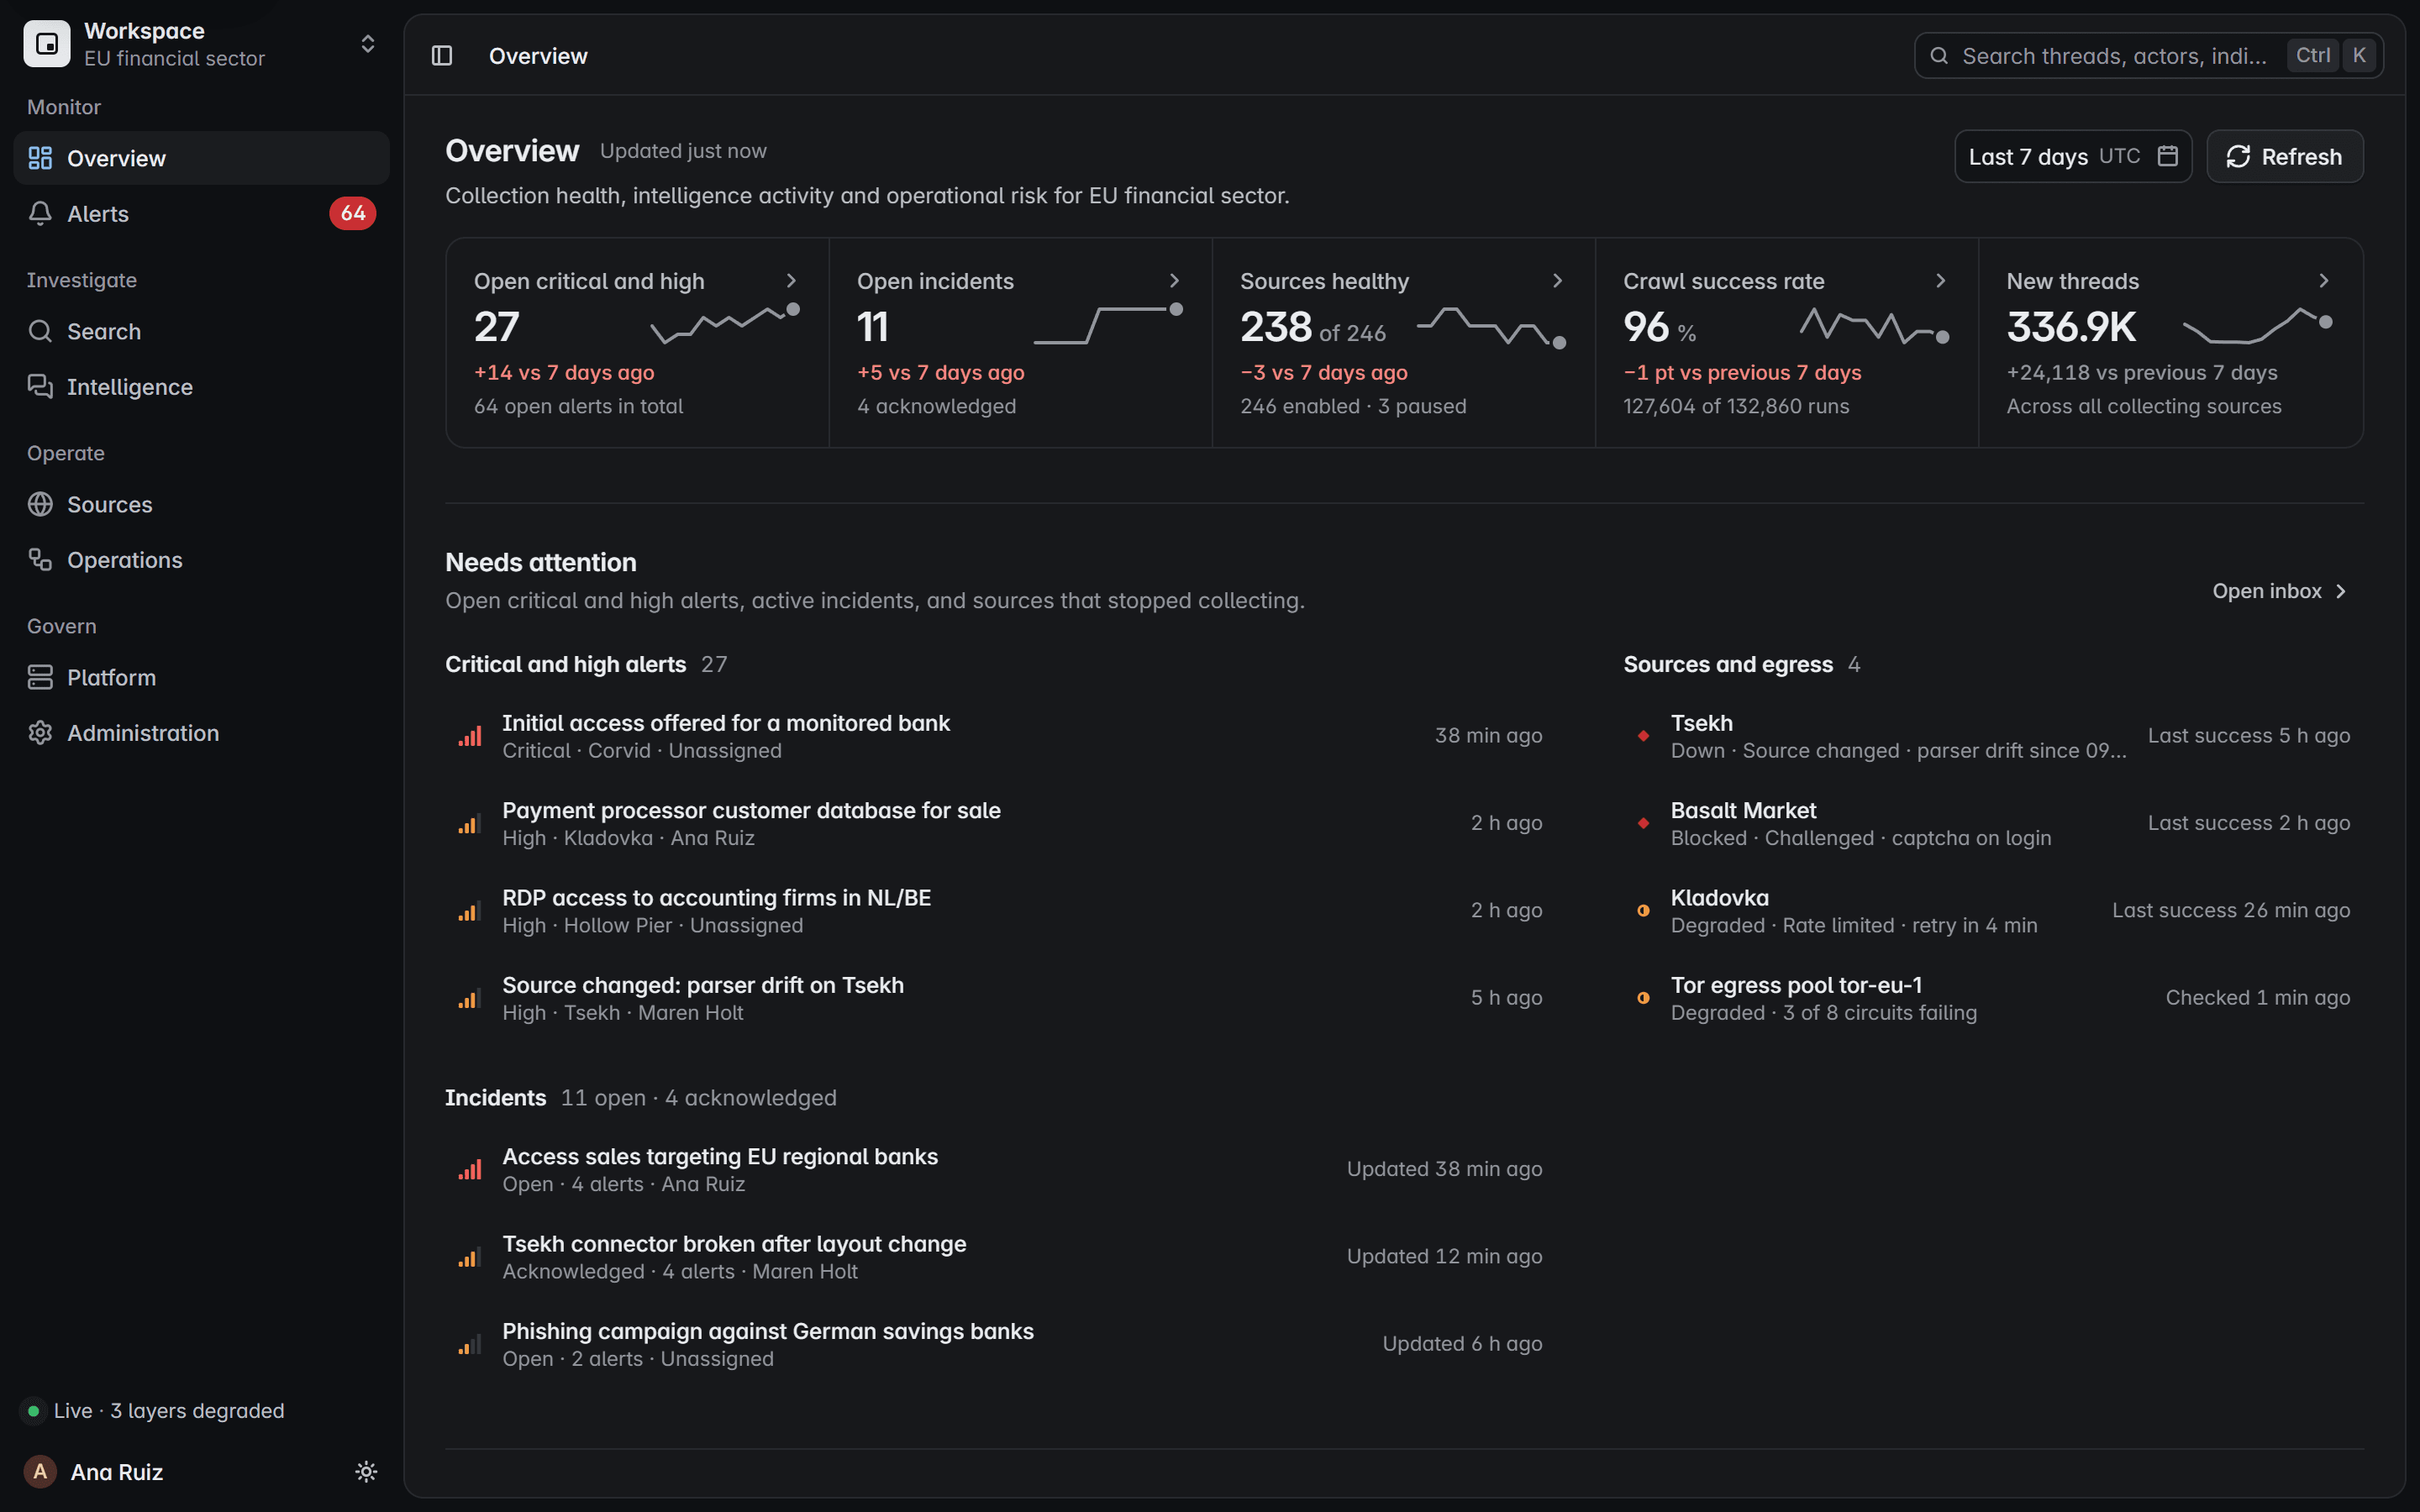
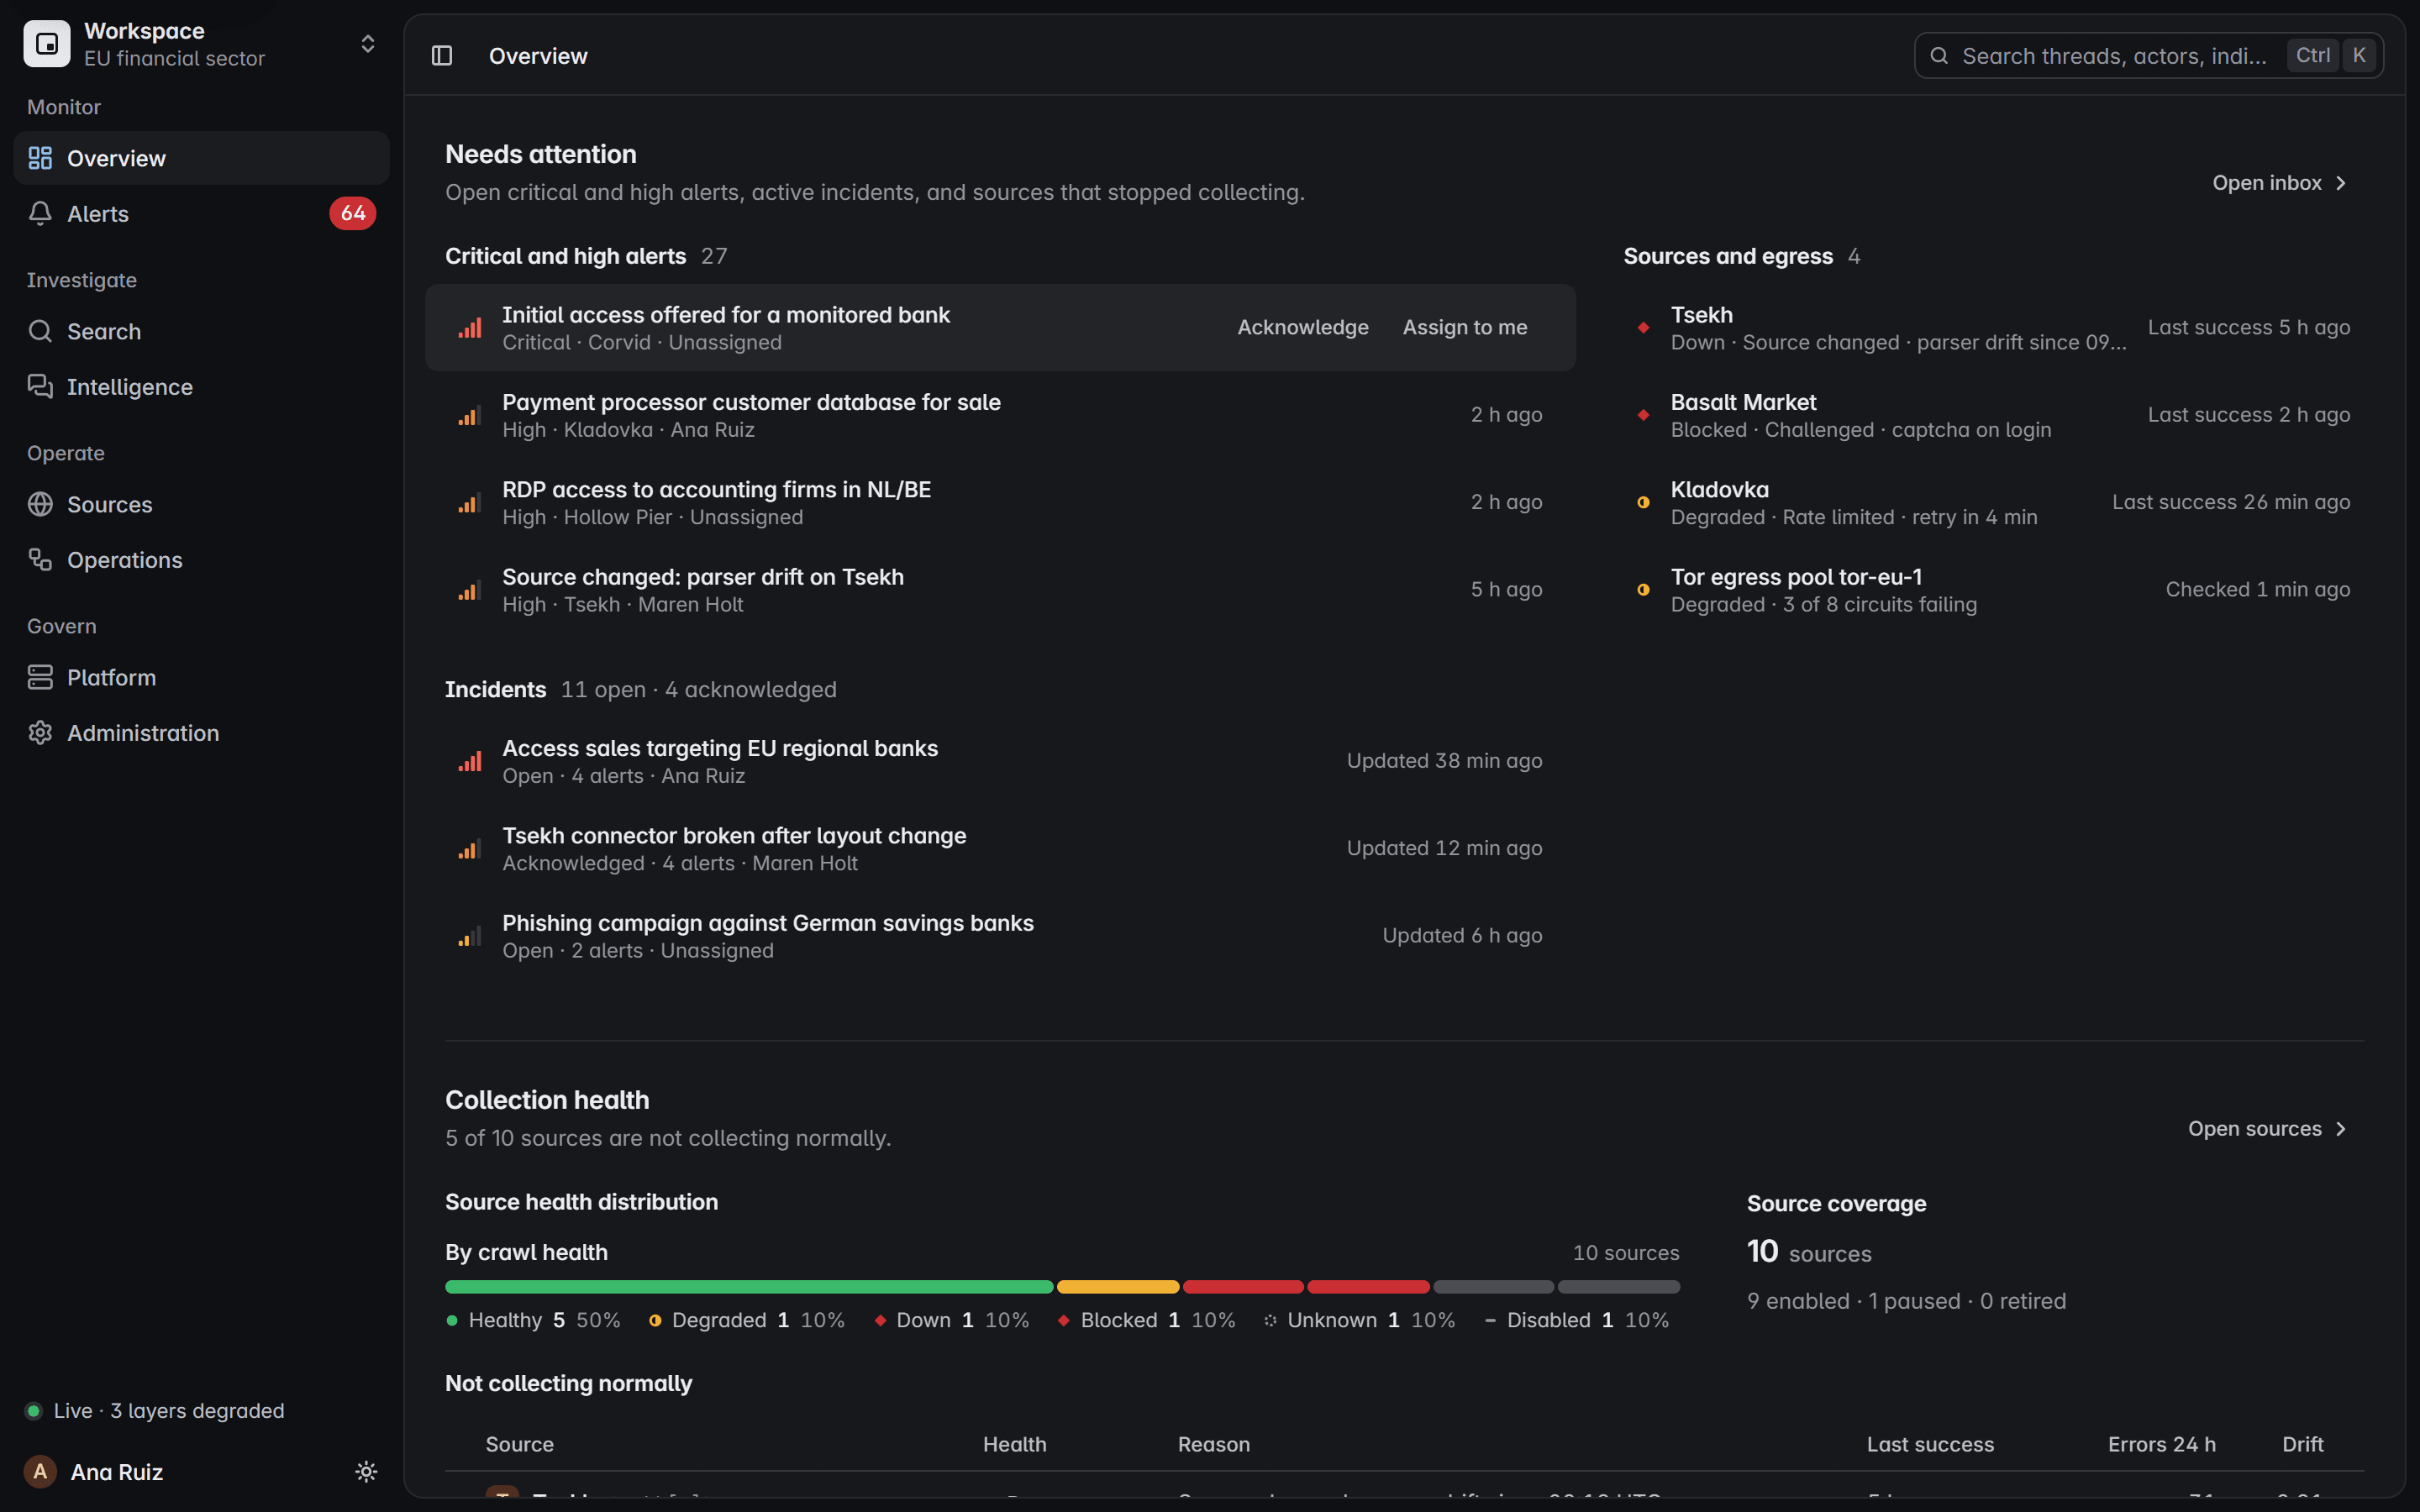
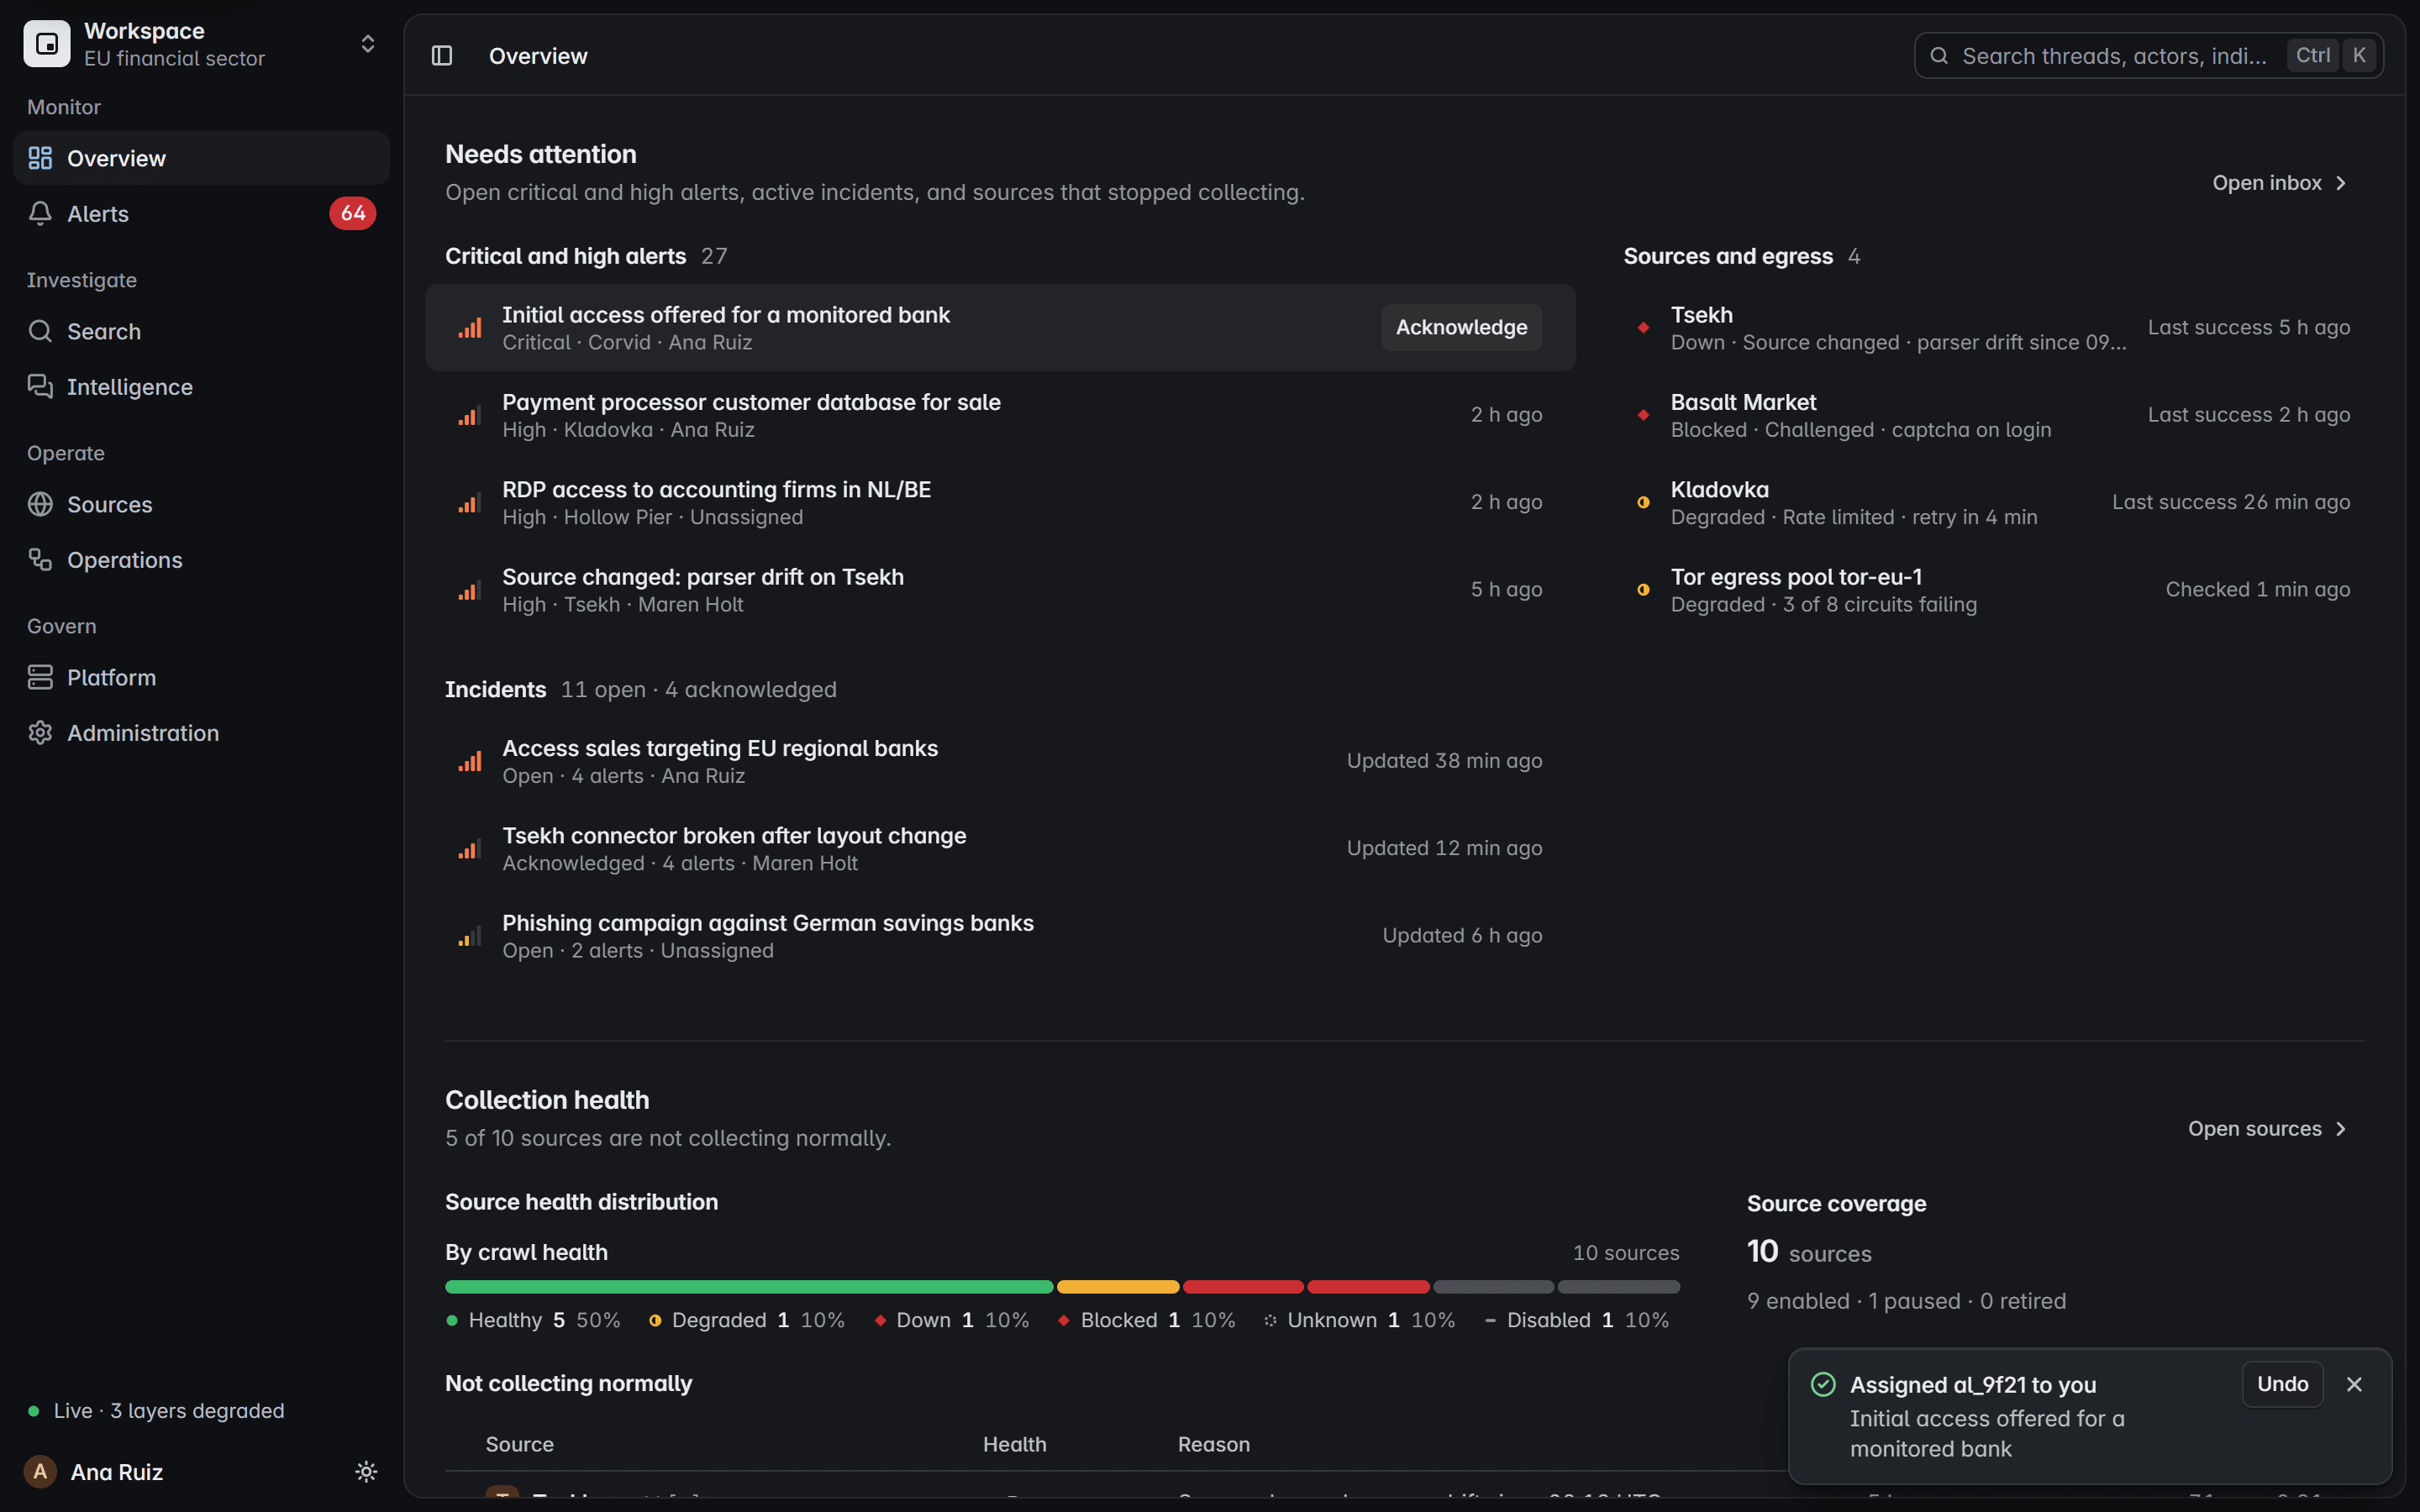
A watchlist matches a post. The alert arrives with its severity, gets an owner and joins an incident. Webhooks tell your own tools.
Watchlists for brands, domains, keywords, actors and indicators match deterministically, and can be replayed over everything already collected.
Critical and high alerts wait in Needs attention, most severe first, with their source and age.
Assign it to yourself or a colleague. Assigning, acknowledging and closing are recorded in the audit trail.
Related alerts are grouped into one incident, with its own owner and state.

Product screen with fictional data
Watch your brand names, domains and the terms fraud runs on. Phishing kits, lookalike domains and customer data offers arrive with their evidence.
The actor behind a phishing kit, the thread that sells it and the lookalike domain, defanged so nothing opens by accident.

A Russian-language sale of a payment service’s customer data, machine-translated and labelled as derived, with the original one click away.
Product screen with fictional data
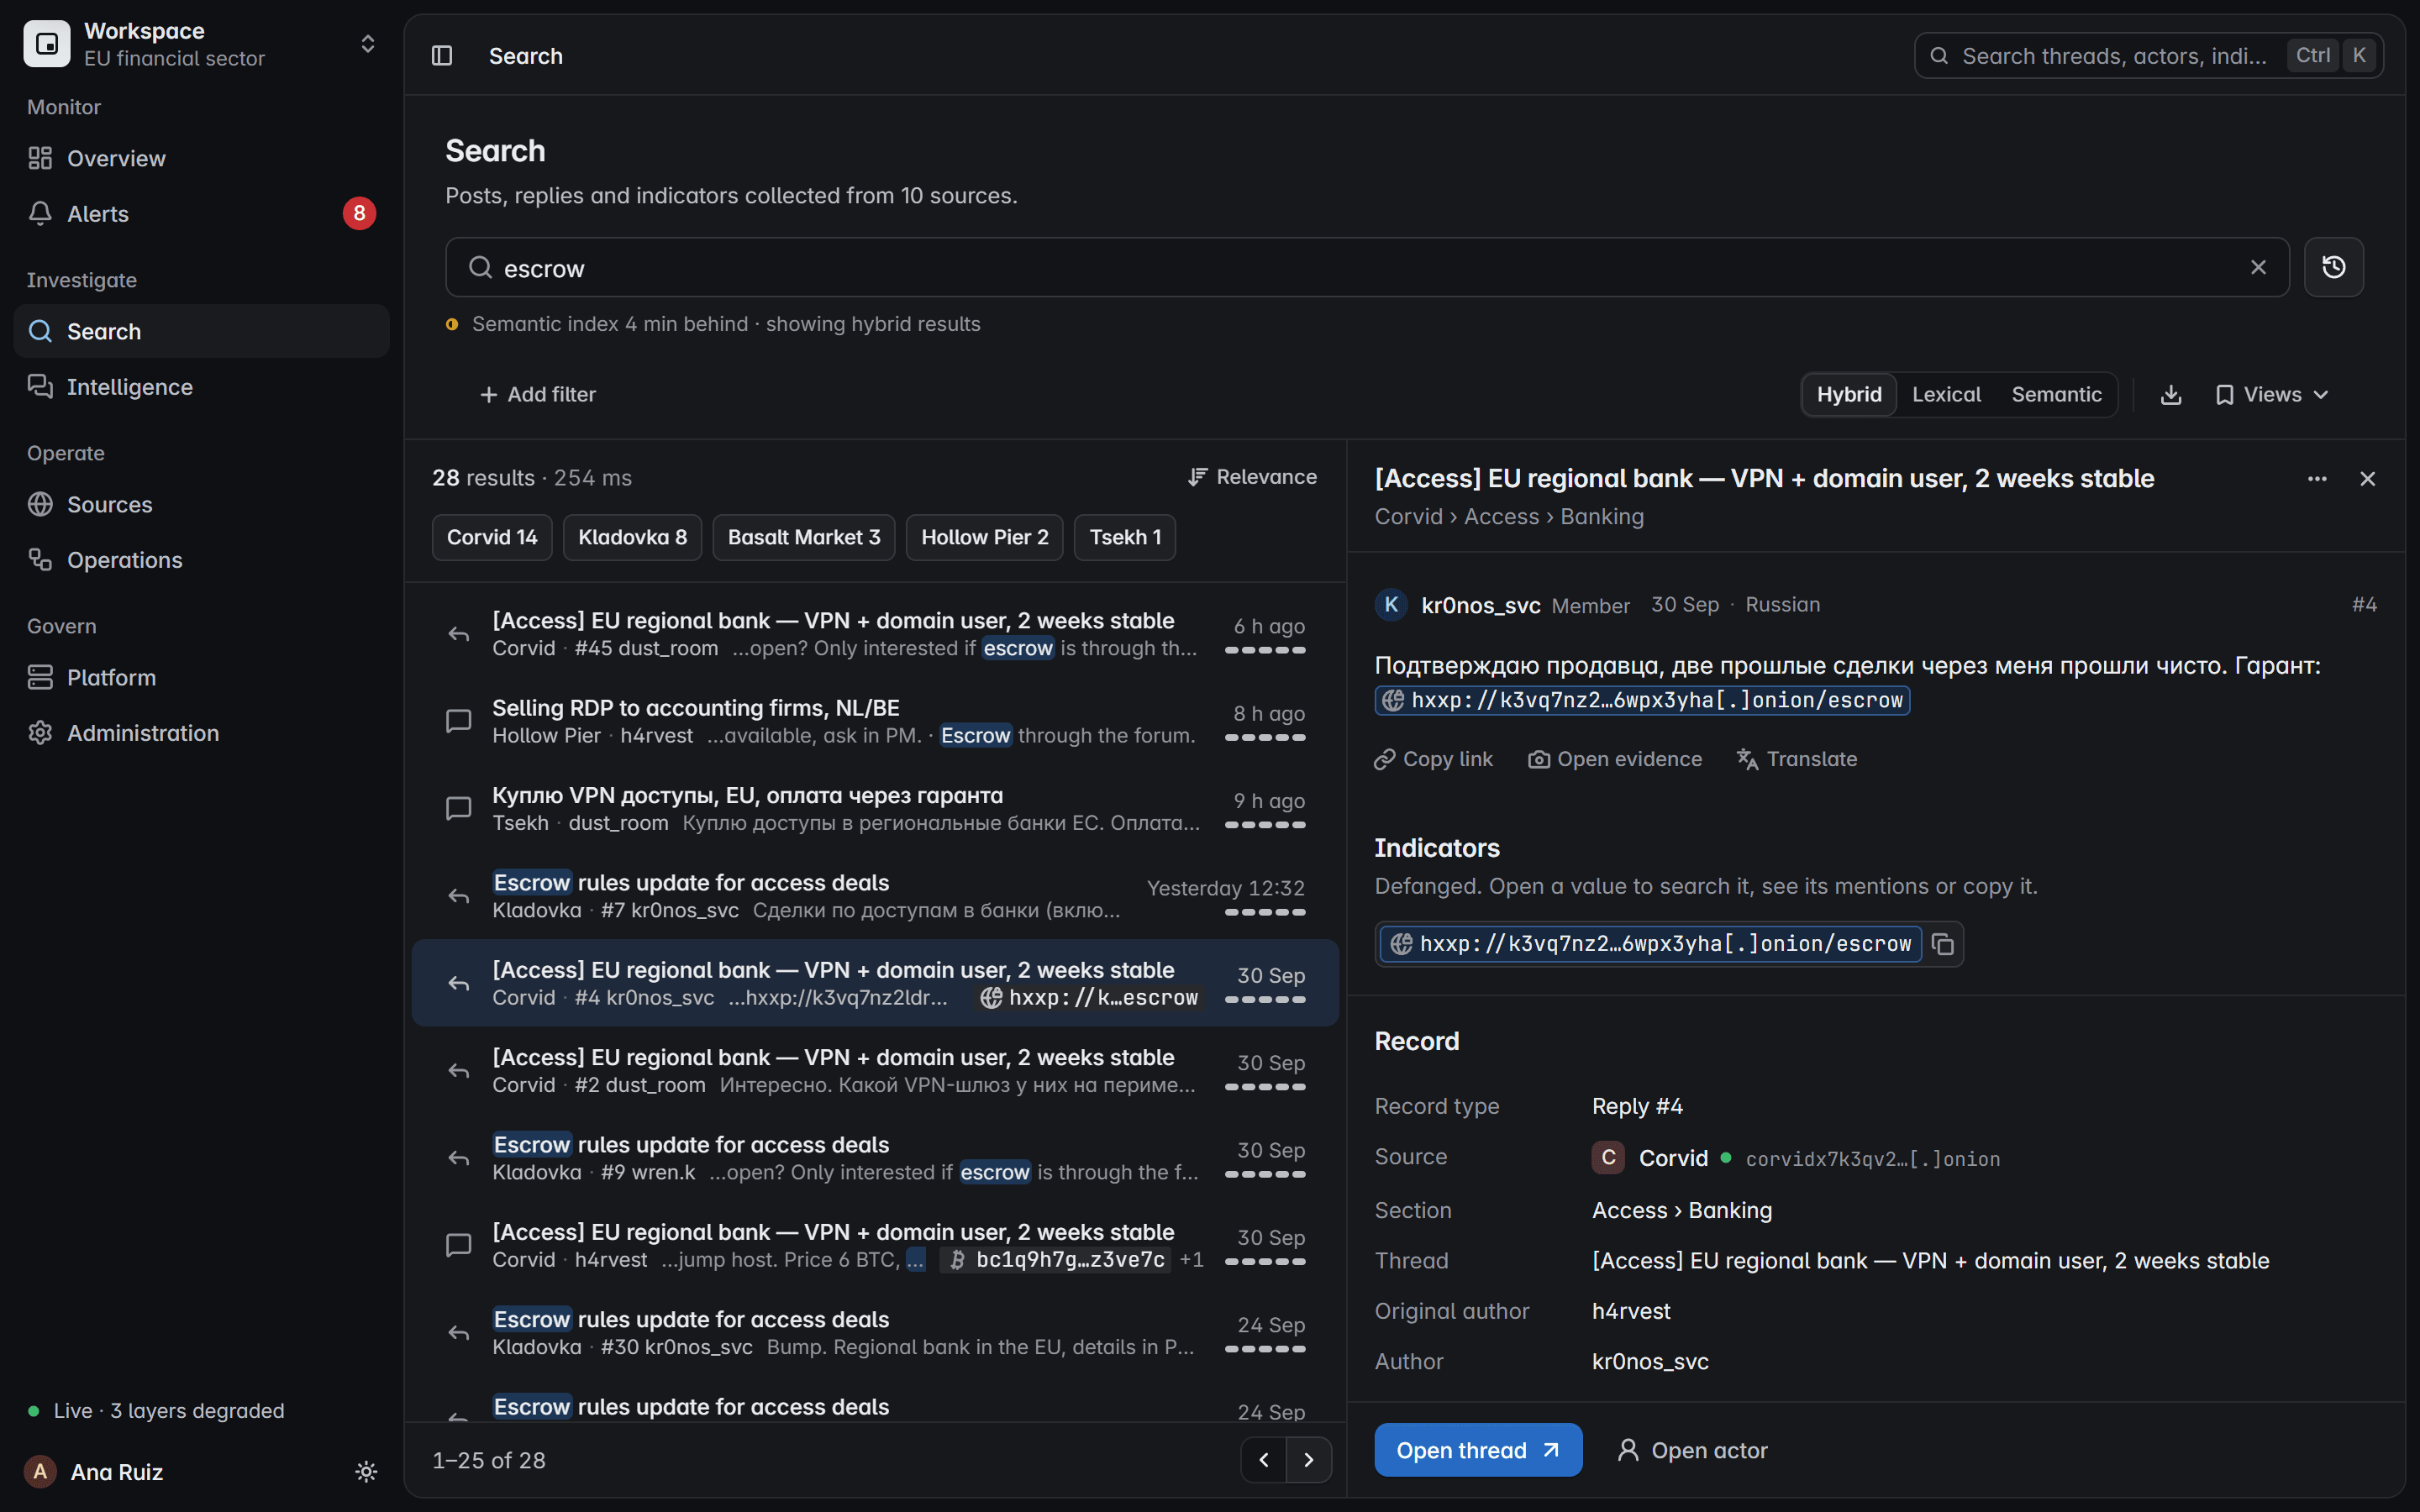
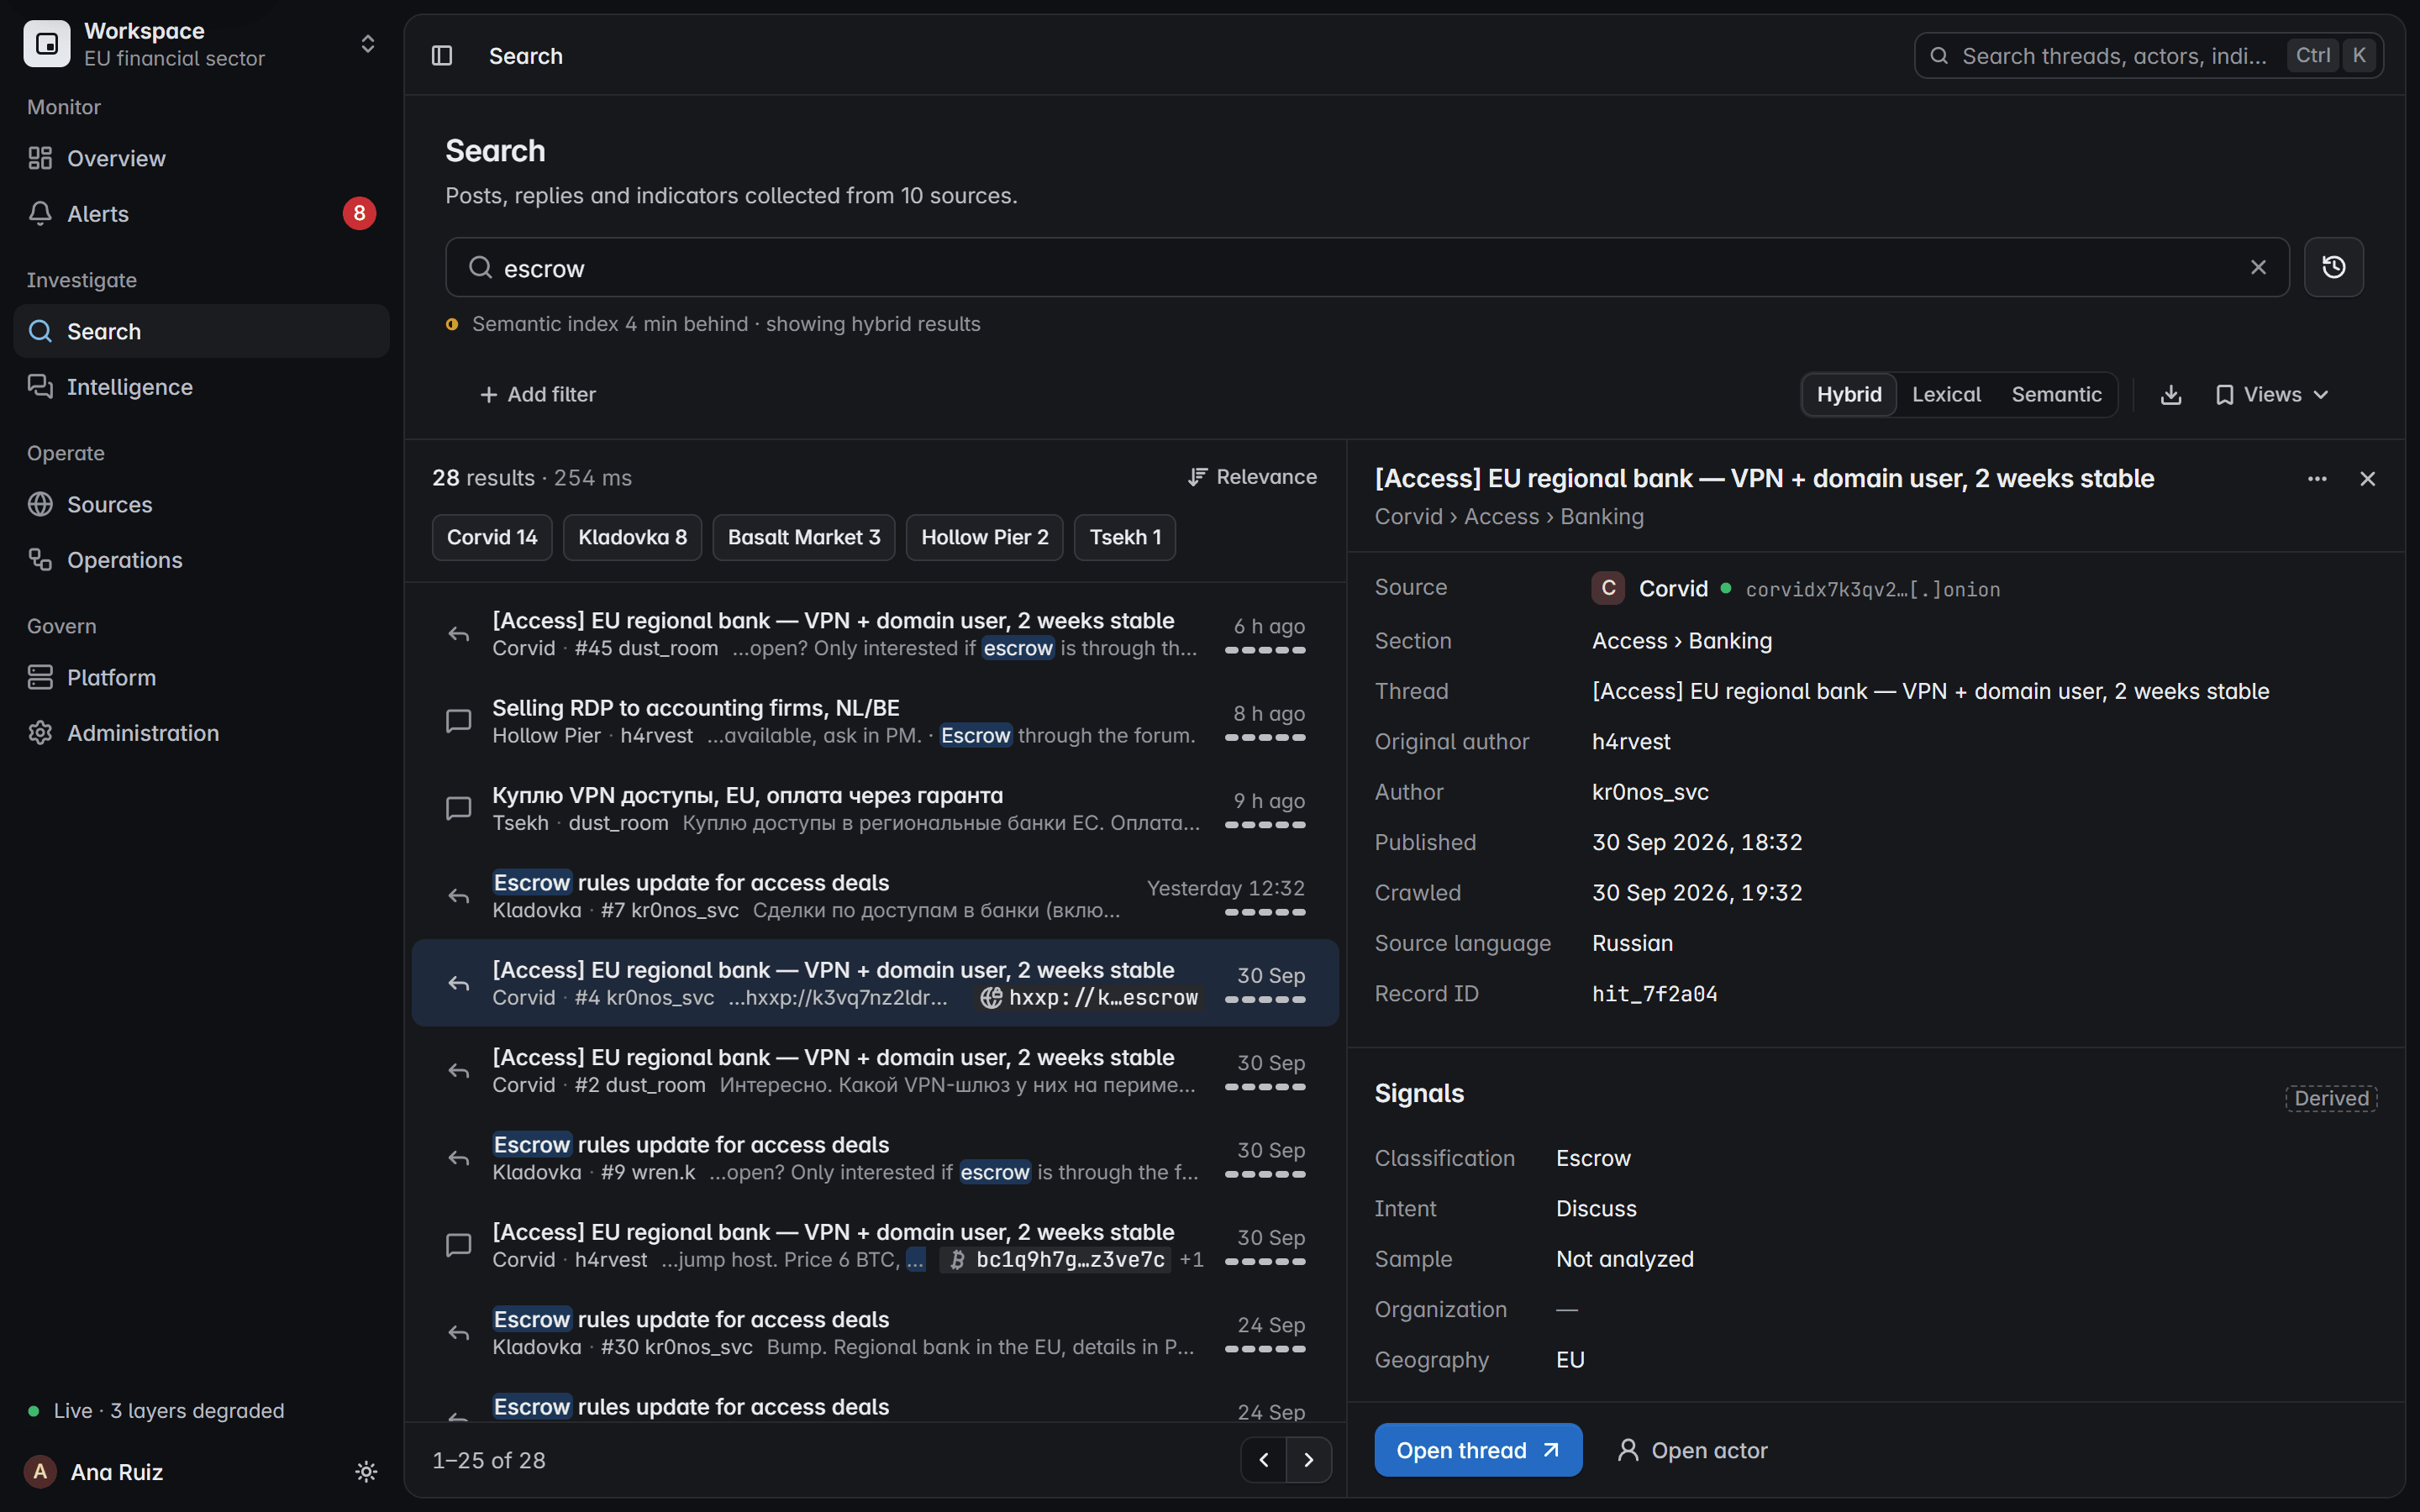
When an incident starts, rebuild the conversation from the record: the original text, both timestamps, the author’s history and the sealed capture.
The post in its original language, with indicators defanged and the capture one click away.
Published is the time the source shows. Crawled is when it was collected. Both are kept.
The author’s aliases, forums, ranks and join dates, as each forum reports them.
Evidence stays sealed, traceable and exportable, so the next reader sees exactly what you saw.
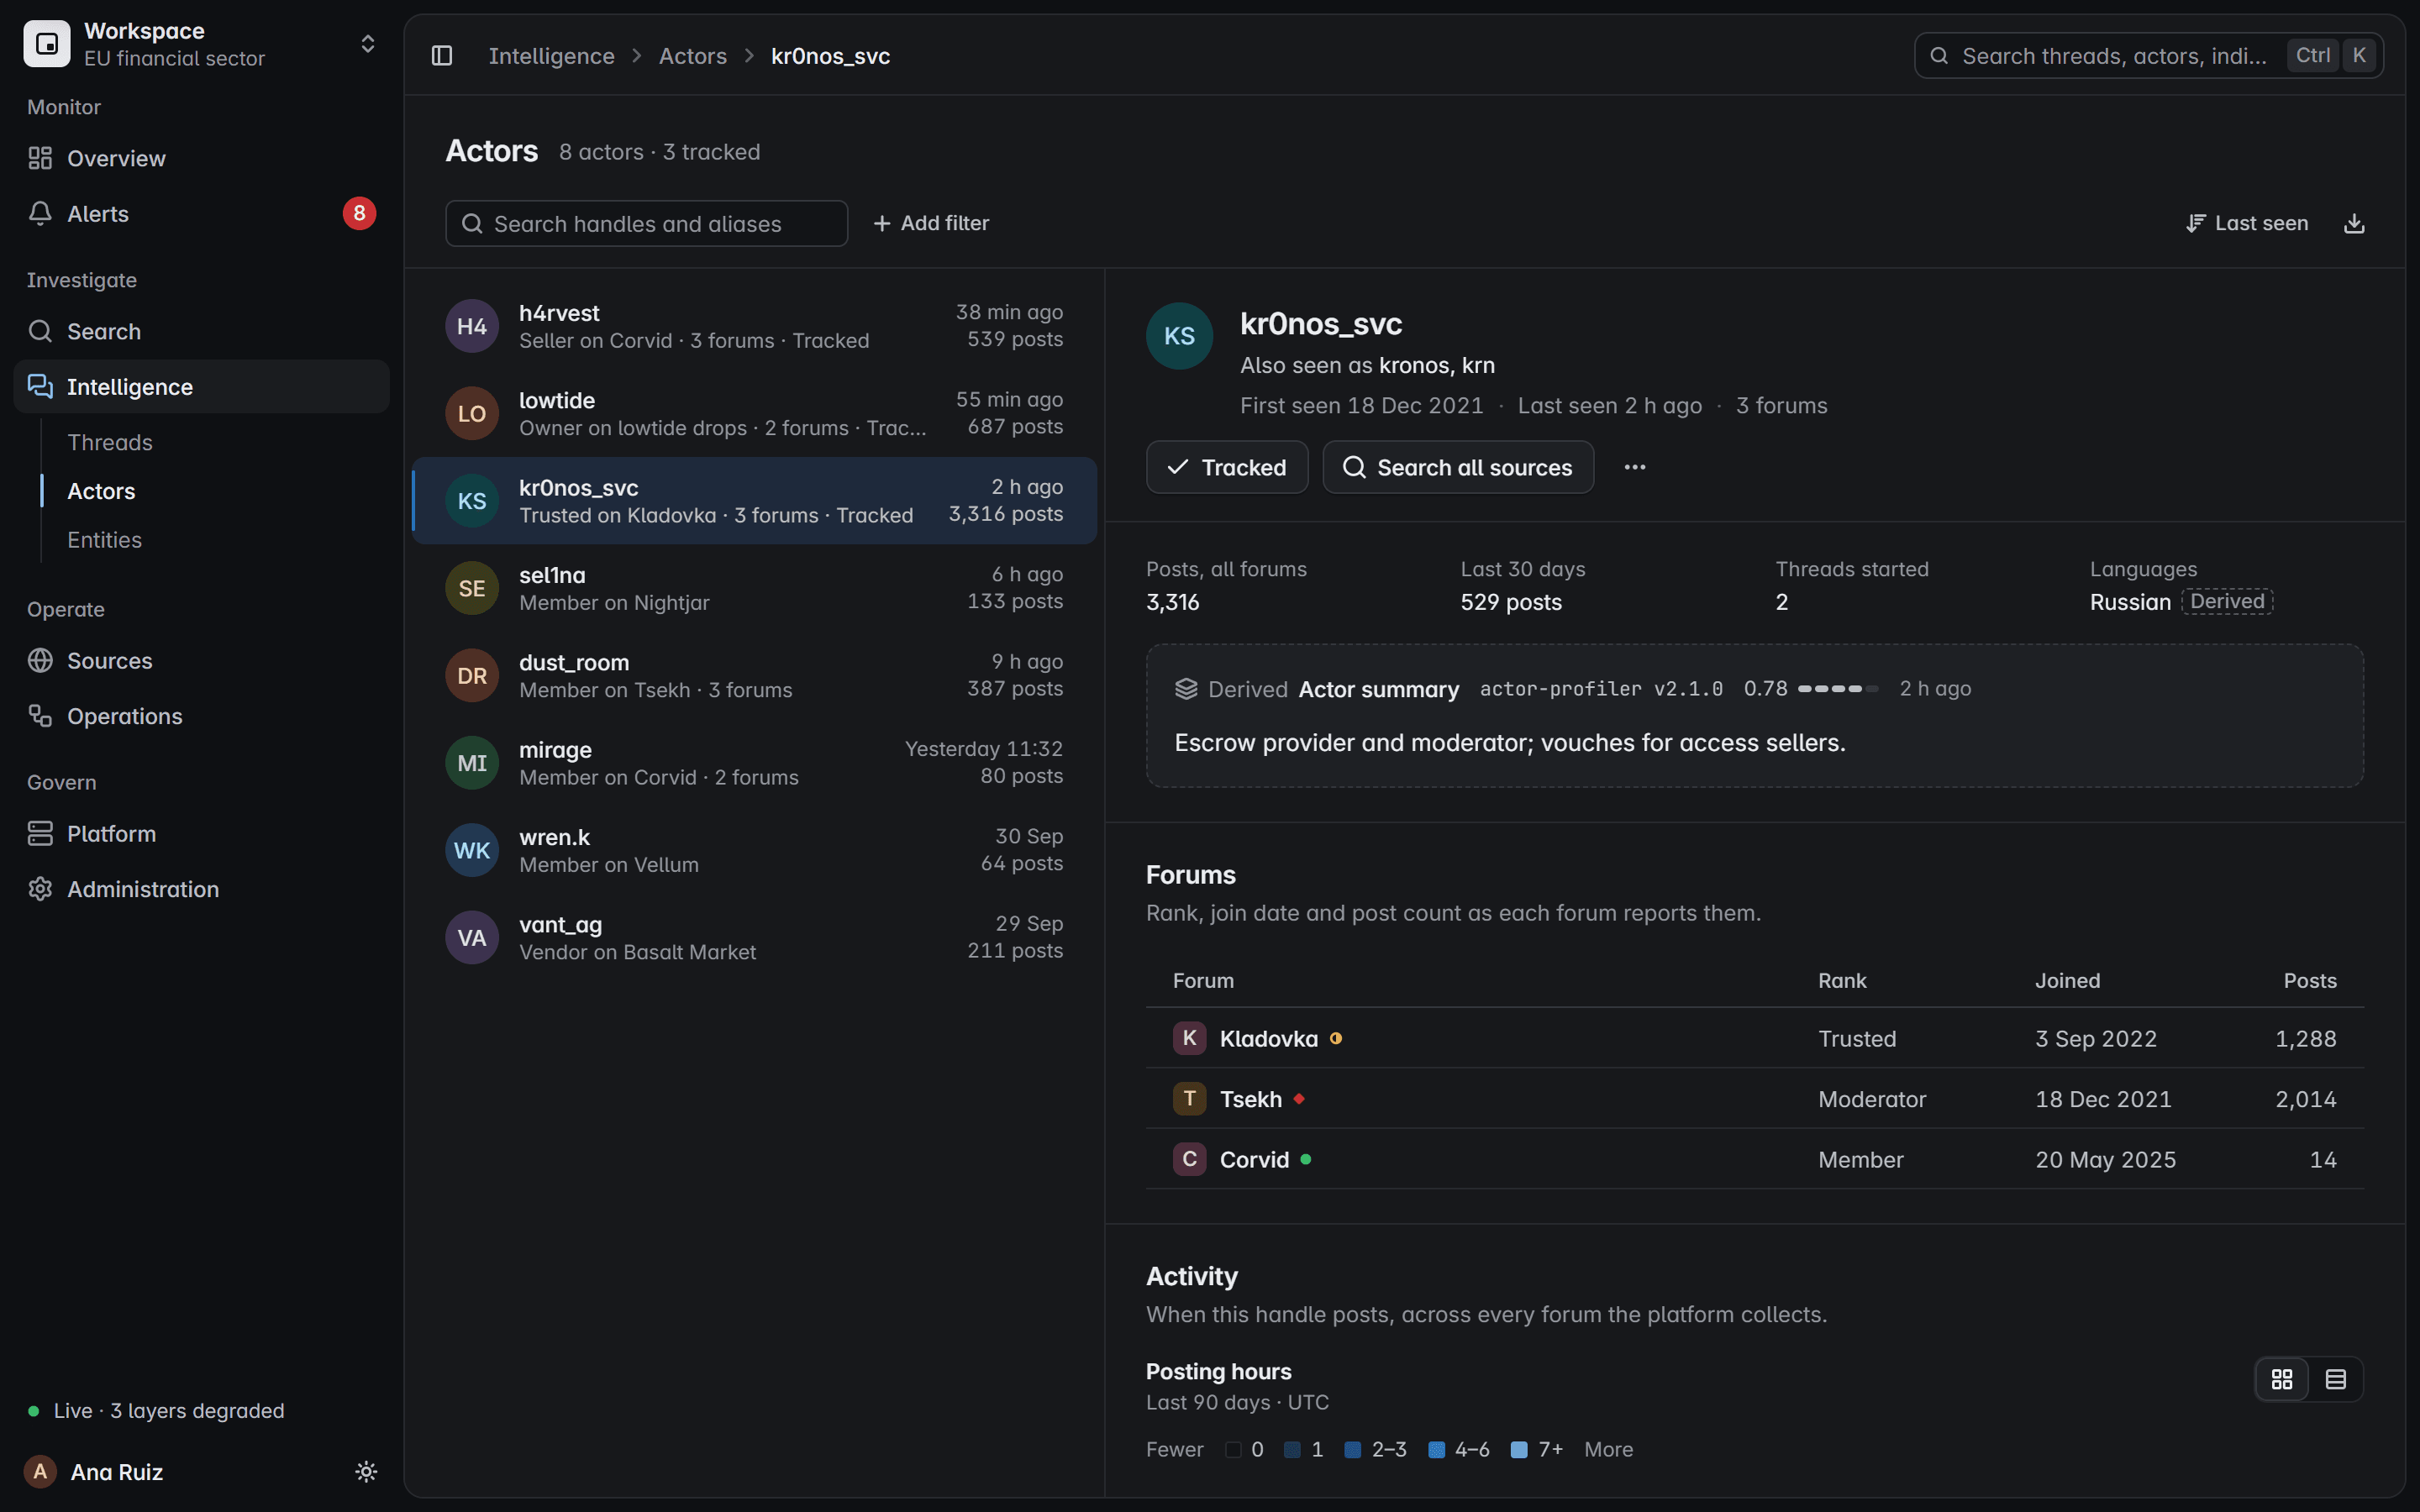
Product screen with fictional data
Add suppliers and partners to a watchlist like any other term. Access sales, insider recruitment and leak-site listings that name them raise an alert.
Remote access to two accounting firms, offered for sale with escrow through the forum.

An actor who recruits insiders at telecom and logistics companies, now on a watchlist.
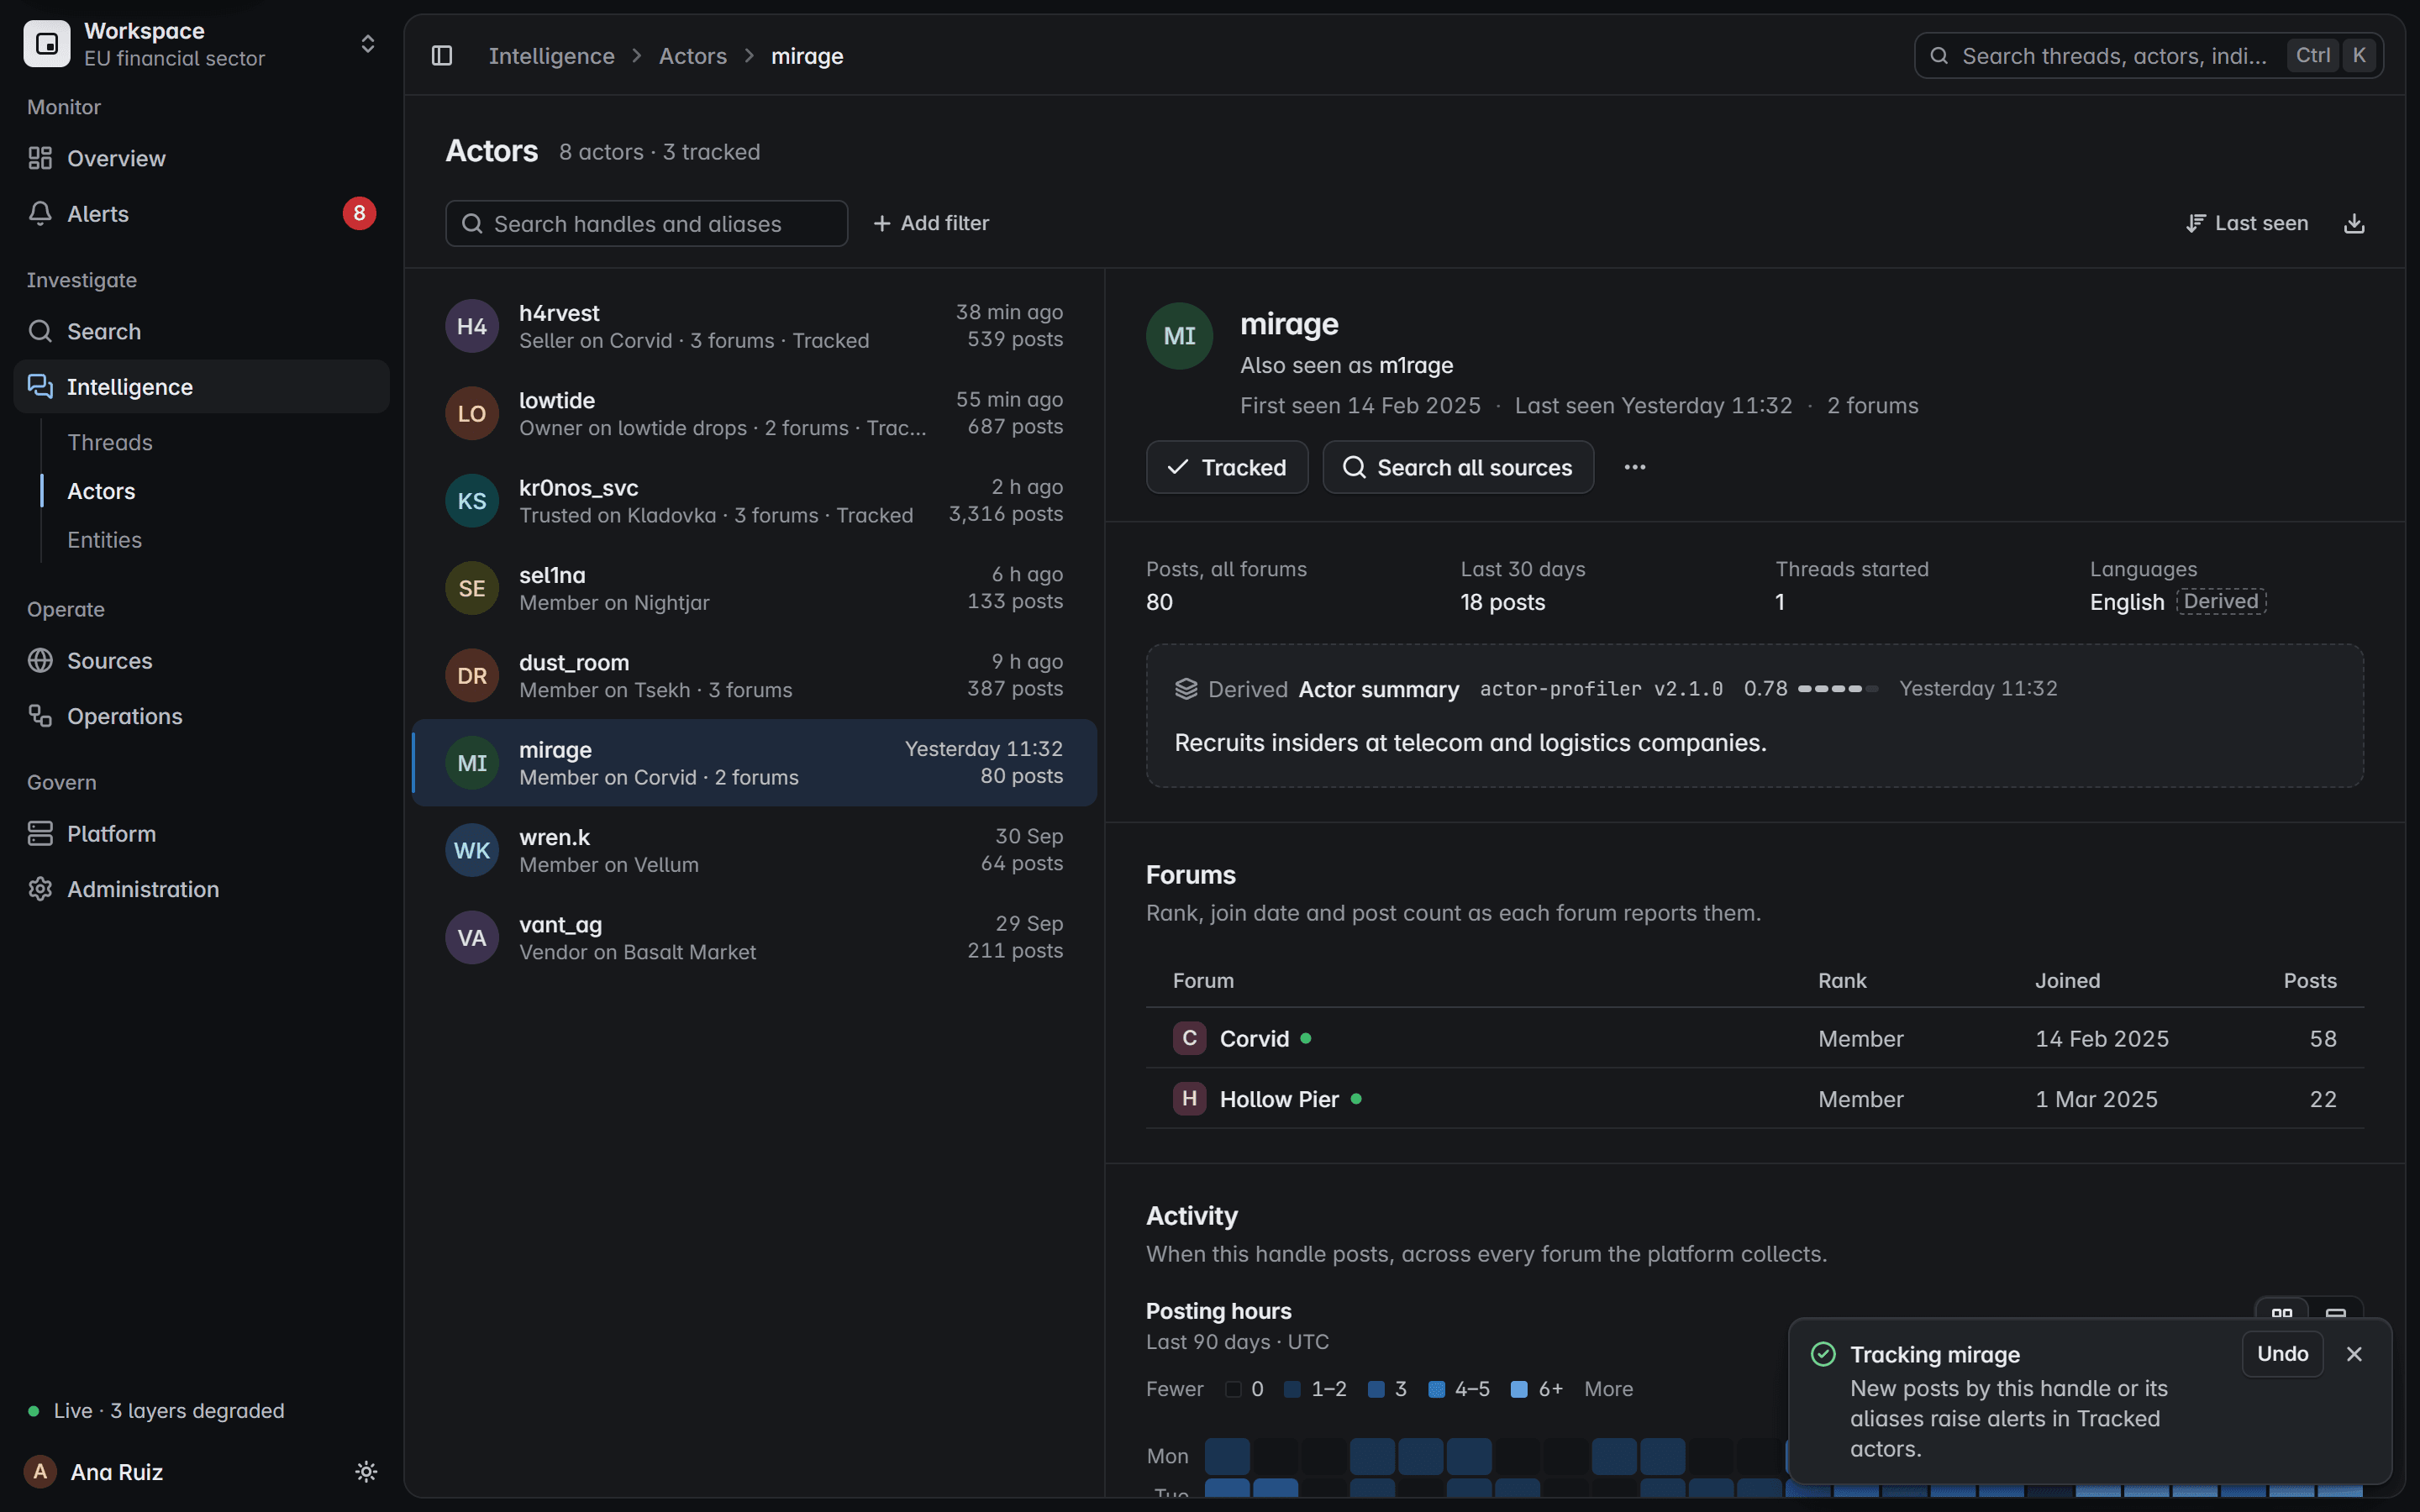
Ransomware victim listings, followed from countdown to removal, without downloading leaked data.
Ransomware leak site monitoringProduct screen with fictional data
Tell us what you need. We will walk you through a live capture, from post to sealed record.
Prefer email? Write to {{CONTACT_EMAIL}}.